Yes—but the job is no longer adequately described as privacy-law compliance alone. Chief privacy officers (CPOs) increasingly advise on artificial intelligence, data governance, cybersecurity regulation, online safety, ethics and product trust. That does not mean one executive should own every technology risk. The durable model is a privacy-led coordinating function with explicit decision rights shared among legal, security, data, product, engineering, risk and AI-governance teams.
What a CPO traditionally owned
The conventional CPO remit centered on the privacy program:
- Interpreting privacy and data-protection laws.
- Setting data-collection, use, retention and disclosure policies.
- Running consumer- or data-subject-rights processes.
- Approving privacy notices, consent mechanisms and records of processing.
- Managing privacy impact or data-protection impact assessments.
- Reviewing vendors and third parties for privacy risk.
- Training employees and advising product, marketing, HR, procurement and engineering.
- Analyzing privacy implications of breaches and coordinating regulator communications.
- Reporting privacy risk to executives and the board.
That work was never purely legal. It required systems knowledge, security cooperation, product judgment and operational controls. What has changed is the scale and number of adjacent decisions that depend on those controls.
Why the remit is expanding
Generative AI and machine learning make data provenance, lawful reuse, profiling, explainability and human oversight immediate operating questions. Cloud and SaaS ecosystems, advertising technology, identity services and data brokers multiply the parties that collect or infer information. Cyber incidents can trigger privacy, contractual, regulatory and customer consequences at the same time. Boards and customers also expect evidence that digital products are safe and responsibly designed, not merely that a policy exists.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errors#1 Best Overall
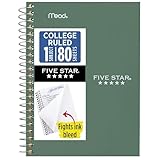
- This 4-3/8" x 7" small size, 1 subject notebook has 80 double-sided college ruled sheets that fight ink bleed and are perforated for easy tear out. Perfectly sized for when you're on the go.
- Tough pockets resist tears and hold loose sheets and notes. Durable plastic water-resistant front cover helps protect your notes and our Spiral Lock wire helps prevent snags on clothes and backpacks.
- All the benefits of our larger notebooks in a smaller, easy to carry size. Sheets measure 4-3/8" x 7 when torn out.
- Available in Seaglass Green
- LASTS ALL YEAR. GUARANTEED!*
These pressures create privacy dependencies and governance interfaces. They do not automatically transfer ownership of security, model risk, ethics or product delivery to the CPO.
What the evidence shows
IAPP’s 2024 Privacy Governance Report found that 80% of respondents had been assigned an additional responsibility alongside existing privacy work. Among those with additional responsibilities, 68% reported added AI-governance responsibilities. In a separate set of figures for surveyed CPOs, 69% reported responsibility for AI governance, 69% for data governance and ethics, 37% for cybersecurity regulatory compliance and 20% for platform liability. Those percentages use different denominators and should not be treated as interchangeable.
IAPP’s 2025 AI Governance Profession Report surveyed more than 670 people in 45 countries and territories. It found that 77% of organizations were working on AI governance, rising to nearly 90% among organizations already using AI. Primary responsibility was split among privacy (22%), legal or compliance (22%), IT (17%), data governance (10%) and security (5%); half of AI-governance professionals sat in ethics, compliance, privacy or legal teams. The report found no single best-practice structure.
Rank #2

- A classroom classic: this 6-pack of 1-subject spiral notebooks helps you identify your subjects at a glance with color-coding efficiency; color assortment may vary
- The right ruling: these 8" x 10-1/2", college-ruled notebooks fit more writing per page than wide-ruled sheets; each notebook provides 70 double-sided sheets with red margin lines
- Perect perforation: Dependable micro-perforated sheets retain your must-have notes but still detach cleanly when you’re ready to revise
- Glide from page to page: Your favorite gel or ballpoint pens will move effortlessly across these smooth pages for A+ notes with minimal ink bleeding or show-through
- 3-Hold punched: Every notebook comes 3-hole punched to fit a standard binder; take along one notebook or several to save extra trips to the locker
IAPP’s 2025 organizational digital-governance report, published November 12, 2025, treats privacy, AI governance, online safety and cybersecurity as intersecting domains. That is evidence of convergence, not proof that one executive now controls them all. A broader professional market is also visible in IAPP’s 2025–26 salary survey summary, which covers privacy, AI-governance and digital-responsibility roles across more than 1,600 respondents in over 60 countries.
Is the CPO becoming a chief trust officer?
Organizations use titles such as Chief Privacy and Trust Officer, Chief Data and Privacy Officer, Chief Privacy, Safety and Regulatory Officer, Chief Digital Responsibility Officer and Chief AI Governance Officer. Those labels can describe four different changes:
| Change | What it means | Main risk |
|---|---|---|
| Title expansion | The executive receives a broader mandate. | Responsibilities grow faster than authority and budget. |
| Functional coordination | Privacy remains distinct while the CPO coordinates adjacent leaders. | Matrix decisions can become slow or ambiguous. |
| Organizational merger | Privacy is formally combined with data, safety, security, ethics or AI. | Conflicting objectives can dilute specialist accountability. |
| Title inflation | More words are added without staff, decision rights or escalation power. | The organization creates accountability without capacity. |
The useful test is not what letters follow the C. Check the reporting line, budget, board access, independence, staffing, remediation authority and product decision rights. A “trust” mandate that cannot stop or escalate a high-risk use case is branding, not governance.
Rank #3

- Perfectly sized for when you're on the go, this small 2 subject notebook has 80 double-sided college ruled sheets that fight ink bleed and are perforated for easy tear out
- Tough pockets help prevent tears and hold 6" x 9-1/2" loose sheets and notes. Durable plastic water-resistant front cover helps protect your notes and our Spiral Lock wire helps prevent snags on clothes and backpacks.
- All the benefits of our larger notebooks in a smaller, easy to carry size. Sheets measure 6" x 9-1/2" when torn out.
- Made with SFI certified paper. Notebook is recyclable – just remove the reinforcement tape on the pocket and recycle the rest! Available in Blue (Color May Vary)
- LASTS ALL YEAR. GUARANTEED!*
CPO and DPO are not interchangeable
A CPO is an organizational leadership position whose scope and reporting line are set by the employer. A data protection officer (DPO) is a legally defined function under the GDPR when the relevant statutory conditions apply. The GDPR requires appropriate expertise, independence, access to the highest management level and protection from conflicts of interest; it does not prescribe one universal reporting-box title. See the primary text at EUR-Lex Regulation (EU) 2016/679 and the contextual overview from IAPP.
One person may hold both titles, but only if the arrangement preserves the DPO’s statutory independence. A CPO can operate the privacy program while an independent DPO performs oversight. Making the DPO the business owner of every privacy decision can create a conflict of interest, particularly where the DPO would determine the purposes and means of processing.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Repair Windows errors before they cause bigger problemsFix Now →Who owns AI governance?
AI governance works best as a responsibility matrix rather than a single-owner slogan.
Rank #4

- LASTS ALL YEAR. GUARANTEED! Guarantee is valid for one year from purchase or delivery date, whichever is longer. Does not cover misuse.
- Scan, study and organize your notes with the Five Star Study App. Create instant flashcards and sync your notes to Google Drive to access them anywhere from any device.
- This 5 subject notebook has 200 double-sided, college ruled sheets that fight ink bleed and are perforated for easy tear out. Sheets measure 8-1/2" x 11" when torn out.
- Tough pockets help prevent tears and hold 8-1/2" x 11" loose sheets. Durable plastic front cover is water-resistant to help protect your notes and our Spiral Lock wire helps prevent snags on clothes and backpacks.
- Made with SFI certified paper. Notebook is recyclable – just remove the reinforcement tape on the pocket and recycle the rest! Available in Pacific Blue.
| Area | Likely accountable function | CPO contribution |
|---|---|---|
| Lawful use of personal data | Privacy and legal | Interpret legal basis, purpose limitation, minimization and rights. |
| Model risk | AI risk, model risk, legal or enterprise risk | Identify privacy and affected-person impacts. |
| AI cybersecurity | CISO and security | Assess exposure, access, monitoring and incident implications. |
| Data quality and lineage | Chief data officer and data governance | Challenge provenance, retention, quality and access controls. |
| Product deployment | Product and engineering | Embed privacy requirements in design and release gates. |
| Bias and discrimination | Ethics, legal, HR, product and risk | Assess rights, affected groups and documentation. |
| Transparency and user controls | Privacy, legal and product | Define notices, explanations and choices. |
| Vendor or foundation-model risk | Procurement, security, legal and privacy | Review contracts, transfers, training data and audit rights. |
| Regulatory reporting | Legal, compliance and privacy | Coordinate obligations and evidence. |
| Enterprise AI policy | Executive committee or board governance | Set privacy and human-rights requirements. |
How privacy should work with the CISO
Security protects systems, identities, infrastructure and information from unauthorized access or disruption. Privacy determines whether data should be collected, linked, used, retained or disclosed in the first place. Resilience limits legal, operational, financial and reputational harm when controls fail. In practical terms, security builds the wall; privacy helps decide what belongs behind it and how much sensitive material is retained. The distinction is conceptual, not a substitute for either discipline.
The CPO and CISO should jointly cover data classification, sensitive-data discovery, minimization, deletion, access management, encryption and key management, logging, cloud architecture, vendor risk, incident notification and tabletop exercises. A breach plan that omits privacy analysis is incomplete, but privacy governance cannot replace technical security controls.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What a modern CPO needs to do the job
- Apply privacy and data-protection law to real products and operations.
- Understand data architecture, lineage, identity, retention and access controls.
- Read enough AI and machine-learning documentation to challenge assumptions about training data, inference and monitoring.
- Quantify risk and explain trade-offs to executives, boards and product teams.
- Design repeatable assessments, approvals, escalation and remediation processes.
- Evaluate vendors, contracts, cloud services and foundation-model dependencies.
- Use ethical and human-rights reasoning without treating ethics as a synonym for legal compliance.
- Influence teams without relying solely on hierarchy.
Most CPOs do not need to become data scientists or security engineers. They do need enough technical fluency to identify control gaps, ask precise questions and know when specialist review is mandatory.
Free tools Windows power users keep installed
One-click scans. No signup required.
Best Value

- BEST-SELLING HARDCOVER JOURNAL: This classic 5.6" x 8" vegan leather journal features a durable and water-resistant cover, 160 college ruled lined pages, inner expandable pocket, sticker labels, ribbon bookmark & elastic closure band.
- PREMIUM PAPER: Made with high-quality, 100 gsm acid-free paper in light ivory color, our journal paper is thicker than average notebooks & note pads, so you can confidently use most pens, pencils, and markers without ghosting and bleed-through.
- LAY FLAT DESIGN FOR WRITING EASE: Our thread-bound, college ruled notebook is designed to lay flat, making it easier to write for both right and left-handed users. It’s the perfect notebook for journaling, note taking and planning.
- INNER POCKET: Includes an expandable inner storage pocket to store appointment cards, notes, receipts, and more. Personalize your journal cover & spine with the sheet of sticker labels included.
- VERSATILE LINED NOTEBOOK: Ideal for journaling, note-taking, planning, or creative writing. Whether you're making a to-do list, capturing ideas, or writing notes, this journal makes a perfect notebook for school, work, or home office.
Metrics that show whether privacy is working
- Percentage of systems and vendors mapped, with accountable owners.
- Time to complete privacy reviews and percentage of high-risk processing with completed assessments.
- Rights-request response time and deletion-control coverage.
- Number and severity of unresolved privacy risks, exceptions and near misses.
- Breach-notification readiness and tabletop performance.
- AI use cases inventoried, risk-tiered and assigned to owners.
- AI systems with documented data provenance, retention and human-oversight controls.
- High-risk team training coverage and remediation time for regulatory inquiries.
- Privacy requirements embedded in product-release gates.
- Projects enabled, redesigned or delayed because of privacy analysis.
IAPP’s reporting on compliance-technology adoption and the warning in “Crunch time: Evolve or face being left behind” both point to the same operating lesson: technology can support evidence and workflow, but it is not a set-and-forget control. Automating an undefined process only produces faster inconsistency.
Choosing an operating model
Traditional CPO with strong partnerships
This fits a smaller or moderately regulated organization with limited AI deployment and mature legal, security and data leaders. It preserves clear privacy accountability and simpler budgeting, but can leave AI and data governance between functions if the CPO lacks product access.
CPO as digital-governance coordinator
This fits a large, multinational or AI-intensive enterprise. The CPO establishes a common risk taxonomy and governance process while specialists retain technical ownership. The price is potential matrix confusion, so escalation and final decision rights must be documented.
Chief Privacy and Trust Officer
This can fit a consumer platform where privacy, safety, ethics and reputation are tightly linked. It gives trust executive visibility, but “trust” must be defined in auditable terms and supported with real staffing.
Federated privacy leadership
This fits decentralized groups with distinct products or jurisdictions. Local expertise improves alignment, but the enterprise needs common controls, tooling, reporting and a clear escalation path to prevent inconsistent decisions.
Questions boards should ask
- Who can stop or escalate a high-risk data or AI use case?
- Is the DPO independent and free of conflicting operational decisions?
- Which executive owns remediation when privacy, security and product priorities conflict?
- Are privacy and AI risks included in enterprise-risk reporting?
- Does the privacy team have technical staff and reliable data lineage?
- Can the organization demonstrate model provenance, retention and user-control evidence?
- Are controls tested, or merely documented?
- Does the budget match the expanded mandate?
The sustainable answer
A CPO is still a CPO: privacy remains the core discipline. The successful CPO now operates as a connector and strategist, involved early in product and data decisions and able to translate privacy, rights and trust concerns into engineering and business controls. The role should broaden in perspective and influence, while technical and operational ownership remains distributed. That is how organizations avoid creating an impossible “everything executive” and still govern data and automated systems responsibly.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




