TRM Labs says it traced more than $35 million in cryptocurrency thefts to attackers exploiting encrypted LastPass vault backups stolen in the 2022 breach. About $28 million was reportedly converted into Bitcoin and laundered through Wasabi Wallet between late 2024 and early 2025, followed by another roughly $7 million wave identified in September 2025.
The key distinction is that criminals did not necessarily obtain every LastPass password in plaintext in 2022. They obtained encrypted vault copies. Some could later be cracked offline, particularly when users protected their vaults with weak, reused, or predictable master passwords. For anyone who stored a cryptocurrency seed phrase or private key in LastPass, changing a password is not enough: exposed wallet secrets must be replaced by moving funds to a newly generated wallet.
What TRM Labs found
According to reporting by The Hacker News, TRM Labs’ blockchain analysis linked more than $35 million in digital assets to theft activity associated with the LastPass breach.
- Approximately $28 million was reportedly converted to Bitcoin and passed through Wasabi Wallet between late 2024 and early 2025.
- A further theft wave of about $7 million was identified in September 2025.
- Reported activity continued into late 2025, including funds reaching a Russian-associated high-risk exchange as recently as October 2025.
- TRM identified patterns involving clustered withdrawals, peeling chains, infrastructure reuse, and continuity of control before and after mixing.
The funds reportedly moved through mixing and laundering services including Wasabi Wallet and Cryptomixer.io, with reported off-ramps including Cryptex and Audia6. TRM assessed that the activity pointed to Russian cybercriminal involvement based on infrastructure and transaction patterns.
#1 Best Overall
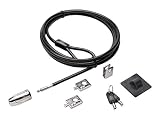
- The strong lock head is designed for desktop PCs and other devices
- 5mm Keying System featuring patented anti-pick Hidden Pin Technology
- 2 adapters and cable trap secure peripheral accessories
- Anchor plate allows devices without a Kensington Security Slot to be locked securely
- 8-foot carbon steel cable is cut-resistant and anchors to desk, table or any fixed structure
That assessment should not be overstated. It does not establish that the Russian government conducted the theft, nor does the available reporting conclusively identify a particular criminal group or individual. Similarly, “more than $35 million traced” is not the same as “exactly $35 million stolen.” Blockchain analysis can identify funds that investigators can confidently connect to known addresses and patterns, but it may miss assets that have not moved or cannot be attributed reliably.
How the 2022 LastPass breach unfolded
The incident involved two connected stages rather than one event in which attackers instantly read every customer password.
- August 2022: An attacker compromised a LastPass developer’s endpoint and accessed the development environment, including source code, technical information, and internal secrets.
- Follow-on targeting: Information from that intrusion was used to target a senior DevOps employee.
- Production access: Malware and captured privileged credentials allowed the attacker to reach cloud storage containing production backups.
- Customer-data theft: The stolen backup data included customer account information, metadata, some unencrypted customer information, and encrypted vault data.
LastPass acknowledged the cloud-backup compromise in its March 1, 2023 technical update. Its earlier security notice warned that attackers could use offline brute-force techniques against stolen vault data.
What information was exposed?
The exposed material could include several different categories of data:
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errors- Names and account information.
- Email addresses, telephone numbers, billing addresses, and IP addresses.
- Account metadata.
- Encrypted password-vault contents.
- Some unencrypted customer information stored in the backup environment.
- Secrets users had placed in their vaults, such as passwords, recovery codes, API keys, cryptocurrency seed phrases, and private keys.
The distinction between encrypted and unencrypted data matters. An encrypted vault is not the same as a readable list of passwords. But a stolen encrypted copy gives an attacker unlimited time to test guessed master passwords away from LastPass’s systems.
Why encrypted vaults remained dangerous for years
An online attack interacts with a live service. It may face rate limits, monitoring, account lockouts, and multifactor authentication. An offline attack uses a stolen encrypted vault file and tests password guesses locally, without repeatedly contacting LastPass.
Rank #2

- Computer lock for HP, Lenovo, Acer, Asus and other brands; not compatible with Dell or Alienware (see part # K68008WW)
- Resettable 4-wheel Number code with 10, 000 possible combinations. Push-button design for one-handed engagement to easily attach lock
- 6’ long carbon steel cable is cut-resistant and anchors to desks, tables, or any fixed structure
- Attaches to laptops, desktops, TVs, monitors, hard drives, docking stations, projectors or any other device featuring a Kensington standard size security slot
- Independently verified and tested for industry-leading standards in torque/pull, foreign implements, lock lifecycle, corrosion, key strength and other environmental condition
A long, unique, unpredictable master password can make offline cracking computationally expensive. A short, common, reused, or predictable password can make it substantially easier. Once a vault is decrypted, an attacker may find credentials that remain useful long after the original breach, including:
- Email and financial-account passwords.
- Exchange credentials.
- Cloud and administrator logins.
- API keys and access tokens.
- Backup codes and recovery codes.
- Cryptocurrency wallet seed phrases and private keys.
This is why the campaign could have a long tail. Attackers could copy vaults in 2022, crack some of them later, and wait before draining dormant wallets or using credentials that victims had not rotated.
Free tools Windows power users keep installed
One-click scans. No signup required.
Multifactor authentication can protect access to a live account, but it does not necessarily protect an already stolen vault backup from offline decryption. Likewise, changing the LastPass master password after the breach does not repair an old vault copy that an attacker has already obtained.
Why cryptocurrency users faced the greatest direct danger
A website password can usually be replaced. A cryptocurrency seed phrase or private key is different: it directly controls the wallet. If an attacker obtains it, the attacker may be able to transfer the assets without accessing the victim’s exchange account, email account, or LastPass account.
Blockchain transfers are generally irreversible. A wallet may also sit unused for years, allowing a criminal to wait until its balance becomes valuable or until the owner stops monitoring it. Moving assets later does not undo the exposure of the old key.
A hardware wallet helps protect a newly generated wallet by keeping signing keys away from an ordinary computer. It does not make an old seed phrase safe if that phrase was previously stored in LastPass. Importing the old seed into a hardware wallet preserves the original exposure.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Rank #3

- 1.12.5" Full HD screen | Delicate picture quality, stunning vision Equipped with 1920 x 1080 Full HD resolution and Wide Viewing Angle technology, the color is full of realism, 178° all-around clear viewing
- Compatible with a wide range of devices: Plug and Play | HDMI/VGA dual interface free switching, support for HDMI and VGA dual input, and can be seamlessly connected with laptops, game consoles, cameras and other devices, no driver required.
- Built-in stereo speakers | synchronized audio and video more immersive, integrated high-fidelity dual speakers, without the need for external audio to enjoy clear sound effects
- Ultra-thin body + portable design | desktop / wall-mounted dual-use * as light as 0.8kg, the thickness of only 5Cm, with no pressure to carry; standard VESA wall-mounting holes, can be used with brackets or wall mounting, easy to create a multi-screen workstations or home audio-visual center.
What former LastPass users should do
If a seed phrase or private key was stored in LastPass
- Assume the wallet secret may be compromised if it was present in the vault during the relevant period and you cannot establish that the vault was protected by a strong, unique master password.
- Use a clean device or a trusted hardware wallet to generate a completely new wallet.
- Transfer the assets to the new wallet.
- Do not reuse the old seed phrase. A new password, new hardware device, or new wallet application does not neutralize an exposed seed.
- Review old addresses and transaction history for unauthorized transfers, including wallets you considered inactive.
Never type the new seed phrase into a website, send it to support, or enter it on a device you suspect may be infected.
Rotate other secrets
Prioritize passwords and secrets stored in the vault for:
- Email accounts.
- Cryptocurrency exchanges and financial services.
- Cloud storage and administrator accounts.
- Business systems and domain accounts.
- API keys, access tokens, recovery codes, and backup codes.
Revoke exposed API keys and tokens rather than merely changing a related login password. Replace recovery and backup codes. Where supported, use passkeys or phishing-resistant hardware security keys for email, exchange, cloud, and administrator accounts.
If cryptocurrency secrets were never stored in the vault
The direct wallet-key risk may not apply, but the breach can still create account and phishing risks. Old reused passwords, exposed recovery codes, API credentials, and customer metadata may help attackers target email, financial, or business accounts. Rotate credentials that remained unchanged and be cautious of messages claiming to offer LastPass recovery assistance.
LastPass has warned that it will not ask users to click links to verify personal information or disclose their master password. Treat unsolicited calls, emails, and messages as potential phishing attempts.
How much does a strong master password help?
A strong, unique master password materially reduces the likelihood that an attacker can decrypt a stolen vault. It does not prove that every other risk is gone. Users should ask:
Rank #4
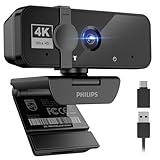
- 【4K ULTRA HD FOR PROFESSIONAL VIDEO】 Upgrade your online presence with 4K resolution. Delivering sharp and vivid image quality, this high-definition webcam ensures crystal-clear, true-to-life video for business meetings and online presentations, helping you maintain a professional edge on screen.
- 【INTEGRATED MICROPHONE FOR COMMUNICATION】 Stay connected effortlessly. The built-in microphone naturally captures your voice for clear daily communication. It provides a reliable all-in-one audio and video solution for your daily Zoom meetings, virtual classes, and casual video chats without needing extra gear.
- 【PHYSICAL PRIVACY SHUTTER & SECURITY】 Protect your digital privacy with a simple slide. This web camera features a built-in physical privacy cover that allows you to mechanically block the lens when not in use. It is a secure solution for your home office, keeping your workspace private and safe.
- 【HASSLE-FREE PLUG AND PLAY SETUP】 Get to work in seconds with no technical skills required. Simply plug the USB cable into your laptop or PC and it is ready to use immediately—no complicated software or drivers to download. A dependable tool designed for a seamless user experience.
- 【UNIVERSAL COMPATIBILITY FOR OFFICE】 Engineered to work flawlessly across major platforms including Windows and macOS. Whether you are using Microsoft Teams, Skype, or Google Meet, this versatile camera is the perfect choice for professional remote work, telehealth, and online teaching.
- Was the master password unique to LastPass?
- Was it long and difficult to guess?
- Was it ever reused or exposed elsewhere?
- Did the vault contain wallet keys, recovery codes, or business secrets?
- Were sensitive credentials rotated after the incident?
If the answer to any of these questions is uncertain, rotating the affected secrets is the safer choice. The presence of multifactor authentication on the LastPass account does not by itself establish that a stolen backup could not be attacked offline.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Business and federated-login exceptions
LastPass said business customers using its Federated Login Services had additional protection because key fragments were held separately and were not included in the stolen backups. That protection depended on the specific enterprise configuration. It should not be generalized to every business account or every LastPass user.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Vault contents created after the attacker’s access window, or information stored only locally and never included in the stolen backups, may have a different exposure. These exceptions do not eliminate the need to investigate what data was actually stored and when.
What remains uncertain
The available reporting does not establish a complete forensic accounting of all losses. Important limits include:
- The number of affected victims is not necessarily the same as the number of wallets linked to the reported funds.
- Some stolen assets may not have moved or may not yet be confidently attributed.
- The exact cracking methods and timelines for individual vaults are not publicly established in the cited reporting.
- TRM’s “traced,” “linked,” and “laundered” terminology describes blockchain-intelligence analysis, not necessarily court-established findings.
- It is not established that every linked theft came from one actor or one criminal group.
The U.K. Information Commissioner’s Office separately announced a £1.2 million fine against LastPass UK Ltd on December 11, 2025, concerning a breach affecting personal information of up to 1.6 million U.K. users. That regulatory action is follow-up enforcement; it is not proof that every TRM-traced theft was directly adjudicated by a court.
The broader security lesson
A password manager can improve security by making unique passwords practical, but a centralized encrypted vault also becomes a valuable target. The right response is not to assume that password managers are automatically unsafe or that a replacement product erases old exposure. It is to match storage to the sensitivity of each secret.
- Use a password manager for unique account passwords and ordinary sensitive credentials.
- Keep particularly consequential cryptocurrency seed phrases outside cloud password vaults if your threat model justifies stronger compartmentalization.
- Generate wallet keys with a reputable hardware wallet or another trusted setup.
- Protect email and exchange accounts with passkeys or hardware security keys.
- Separate recovery information so one compromised vault does not expose every path to an account.
- During an incident, replace irreversible secrets rather than merely changing passwords.
Products such as Ledger, Trezor, and GridPlus offer hardware-wallet options, but none can repair an exposed seed phrase. Password-manager alternatives such as Bitwarden, 1Password, and Proton Pass may offer different encryption, recovery, audit, and secret-separation designs, but switching services without rotating old secrets does not solve the original problem.
For account protection, hardware security keys from Yubico and passkey support from major account providers can reduce phishing and credential-reuse risk. They still cannot invalidate a cryptocurrency private key or protect a vault copy that was already stolen.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




