Non-human identity management (NHI management) is the practice of finding, governing, securing and retiring the digital identities that software uses to authenticate and access systems. These identities belong to things such as applications, services, cloud workloads and AI agents—not people—and often need to be created, changed or removed as software is deployed and automated.
What counts as a non-human identity?
The Cloud Security Alliance (CSA), in a definition released July 22, 2026, describes a non-human identity as an identity principal that can authenticate and be authorized, directly or indirectly, to access resources. The principal is the digital identity being granted access. A configuration record or a piece of code that cannot authenticate is not automatically an identity.


It is also important to distinguish an identity from its credential. A credential is what an identity uses to prove itself; one identity may use different credentials for different actions. Industry discussions sometimes use “identity” loosely for a key or token, so check what a particular system means.
| Example | How it fits |
|---|---|
| Service account, application principal or service principal | The identity principal representing an application or service when it requests access. |
| Workload identity | The identity associated with a running workload, such as an application or automated process. |
| AI agent | A software identity that may act autonomously and access resources, sometimes delegating tasks to sub-agents. |
| API key, OAuth token, certificate, SSH key or secret | Usually a credential used by an identity, not the identity itself. Its role depends on how the particular system represents principals and authentication. |
Microsoft uses “machine identity” for a specialized subset of non-human identities that secures communications among devices, servers or virtual machines. The terms overlap, but they are not necessarily interchangeable in every system.
#1 Best Overall
Why ordinary employee IAM is not enough
Human identity processes commonly follow business events: hiring, job changes and departure. Software identities are more often created or changed by technical events such as application deployment, infrastructure provisioning, workload startup, pipeline execution, autoscaling or an agent being invoked. Device identities may also follow asset onboarding and decommissioning.
As a result, an HR-driven joiner-mover-leaver process will not, by itself, find and retire every software identity. A service can remain active after a project ends, or a workload can change while retaining access it no longer needs. NHI management connects identity controls to those technical lifecycles.
Rank #2

- POWERFUL SECURITY KEY: The Security Key C NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key C NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key C NFC via USB-C and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
How NHI management works across an identity’s lifecycle
- Discover and inventory. Find identities across the systems and environments they use, and associate each with the workload, application or business purpose it supports.
- Assign ownership and provision access. Record who is accountable for the identity, why it exists and what it needs to do. Grant only the access required for that task.
- Monitor activity and review access. Check how identities are used and whether their permissions still match the workload as it changes.
- Manage credentials. Prefer platform-managed identities or short-lived credentials when the architecture supports them. Rotate or revoke credentials that are exposed or no longer needed.
- Decommission cleanly. When a service, pipeline, project or integration ends, remove the identity and revoke its associated credentials.
This is an operating lifecycle, not a single-product feature. The CSA distinguishes governance—which sets policy and accountability—from management, which carries out provisioning, maintenance and deprovisioning. It recommends treating NHI governance as part of enterprise risk management. In practice, identity governance, cloud IAM, workload identity, secrets and certificate management, and monitoring may each cover different parts of the lifecycle.
Controls that reduce risk
Give every identity a purpose and an owner
An inventory is more useful when it explains what each identity supports and who is responsible for it. Without that context, it is harder to tell whether an identity is still needed or whether its access is appropriate. The CSA and NHI Management’s lifecycle guidance both emphasize accountability and inventory.
Quick wins for a faster PC:
Scan for outdated or missing drivers - takes under a minuteDriver Scan →Clear out junk files and repair common Windows errorsFree Scan →Limit and review permissions
Grant an identity only the access needed for its task, then review it when the workload or its responsibilities change. Microsoft recommends least-privilege access for machine identities. Reviewing permissions helps catch access that has accumulated as a system evolved.
Reduce exposure from long-lived credentials
Where supported, managed identities can let workloads authenticate to cloud services without storing passwords, API keys or access tokens, according to Microsoft. Short-lived credentials can also reduce the time a stolen credential remains useful. These approaches depend on the architecture; they do not remove the need to protect, monitor and revoke credentials when circumstances require it.
Rank #4

- IAM REFERENCE POSTER: Features key Identity and Access Management terms and signals including Principal, Credential, Entitlement, Policy Decision, Approval Flow, Session Token, Assertion, Access Log, and Audit Event.
- CRISP GLOSSY PRINT: Printed on high-quality glossy paper at 13x19 inches in portrait orientation, delivering sharp, clear visuals ideal for professional display.
- VERSATILE DECOR: Perfect for offices, classrooms, training rooms, and tech workshops, making it a great addition to any IT or security-focused environment.
- EDUCATIONAL TOOL: Designed for IAM teams, security architects, and enterprise IT professionals to support team discussions, training sessions, and knowledge sharing.
- UNFRAMED AND READY TO DISPLAY: Arrives as a single unframed poster, easy to frame or mount in your preferred style to suit any workspace aesthetic.
Connect retirement to technical change
Build identity removal into the processes that retire services, pipelines, projects and integrations. Removing a workload without disabling its identity or revoking its credentials can leave access behind. Device identity retirement should likewise follow asset decommissioning.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Why AI agents make identity governance more urgent
An AI agent may take actions autonomously, encounter new resources, or delegate work to sub-agents. Those behaviors make it important to know which identity is acting, what it can access and how its permissions are evaluated. Microsoft identifies short-lived credentials, real-time policy evaluation, accountability and auditability, and human oversight for sensitive tasks as relevant controls. These are current considerations, not a universal technical standard.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Best Value
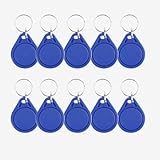
- NOTE: These are 13.56 MHz key fobs (tags). If you want to register them to your lock system, please make sure your system uses the same 13.56 MHz frequency.
- Durable Material: Made of high-quality ABS waterproof material, lightweight and durable, equipped with a metal key ring for easy carrying and use.
- Wide application: Suitable for apartments, office buildings, factories, communities, parks and other access control places.
- Stable performance: operating frequency 13.56MHz, sensitive sensing, reading distance up to 0-10cm, and fast recognition.
- Suitable for use with 13.56MHz RFID proximity access control and identity management systems. For example, it can be registered as a new key in an RFID door lock, where applicable.
A CSA whitepaper published in May 2026 frames agent identity as a governance challenge, including the possibility that delegation creates identities and permissions for sub-agents. Palo Alto Networks’ Wendi Whitmore, Chief Security Intelligence Officer, described the issue this way: “While attackers utilize AI to scale and accelerate threats across a hybrid workforce, where autonomous agents outnumber humans by 82:1, defenders must counter that speed with intelligent defense.” The 82:1 figure is a vendor-research statement, not a universal count or a directly interchangeable measure with other NHI ratios.
What published NHI figures do—and do not—show
Published estimates illustrate why organizations are paying attention, but they use different scopes and measures. They should not be treated as a prediction of the ratio or exposure in any particular organization.
| Finding | Attribution and scope |
|---|---|
| 144 non-human identities for every human identity, up from 92:1 in the first half of 2024 | Entro Security, as reported by the CSA’s 2026 whitepaper; cloud-native environments. |
| About 45:1 average NHI-to-human ratio | Entro Security, as reported by the CSA’s 2026 whitepaper; enterprise environments. |
| 44% growth in the industry NHI population from 2024 to 2025 | Entro Labs, as reported by the CSA’s 2026 whitepaper. |
| 28.65 million hardcoded secrets added to public GitHub repositories in 2025 | GitGuardian, as reported by the CSA’s 2026 whitepaper; public repositories, not all secrets or all environments. |
The CSA notes that reported ratios vary, and the figures above describe different populations and findings. They are useful as attributed study results, not universal benchmarks.
How to assess an NHI management approach
Organizations comparing tools or processes can ask whether they cover the identity types and environments actually in use, including applications, workloads, devices and agents. They can also assess whether an approach can:
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
- discover identities and connect them to an owner and purpose;
- support least-privilege permissions and access reviews;
- manage credential lifecycles, including short-lived identity options where available;
- monitor activity and provide auditability;
- automate provisioning and decommissioning; and
- integrate with existing IAM, cloud and secrets systems, as well as relevant AI-agent workflows.
These are evaluation criteria drawn from the lifecycle and governance needs described by the CSA, Microsoft and NHI Management, not a benchmark of specific vendors. The right mix depends on the organization’s systems and how its software identities are created and used.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




