Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Boards need cybersecurity measures that change business decisions—not a parade of blocked attacks, alert counts or training completions. A useful board dashboard shows which business services could be harmed, how exposed they are, whether controls reduce that exposure, whether the company can recover, and what decision management needs from directors.
This approach follows NIST’s measurement guidance, which stresses measures that support operational and senior-level decisions (NIST cybersecurity measurement; NIST information-security measurements). NIST CSF 2.0 also places cybersecurity governance inside enterprise risk management through its Govern function (NIST CSF 2.0).
The five questions every board dashboard should answer
- What could materially harm the business? Identify revenue-critical services, sensitive data, safety obligations, strategic dependencies and regulatory commitments.
- How exposed are we now? Show exploitable weaknesses, attack paths, identity gaps, supplier dependencies and unsupported technology affecting those priorities.
- Are controls working? Measure control coverage and effectiveness against defined scenarios, not simply whether a tool is deployed.
- Can we detect, contain, continue and recover? Test response, restoration and continuity against stated objectives.
- What decision is required? Every material exception should have an owner, treatment plan, date, funding request or explicit residual-risk acceptance.
A security-operations dashboard optimizes daily work. A board dashboard explains business consequence, trend, uncertainty and accountability.
Six metric families for a board-level view
1. Business-critical exposure
Start with the services whose interruption would affect revenue, customers, operations, safety, legal obligations or strategic plans.
#1 Best Overall

- Keep your notes and assignments in order with this hybrid NoteBinder. Five dividers organize handouts by subject, so you can find what you're looking for in a flash.
- Durable plastic covers protect pages from damage and fold back to lie flat when taking notes. Clearview cover allows you to personalize the binder with a custom cover sheet.
- TechLock rings open easily and firmly hold sheets in place with a flexible design that withstands frequent use.
- 1" rings hold up to 200 sheets of letter-size (8 1/2" x 11") paper.
- 2 NotePocket dividers offer additional space for handouts and other loose papers. 3 NoteProtector dividers make it simple to organize the binder, so documents can be found in an instant.
- Percentage of critical services with a named business owner, documented recovery objective, current dependency map and tested continuity plan.
- Number and criticality of internet-facing assets without an owner, unsupported systems, crown-jewel applications without tested recovery and critical suppliers without current assessments.
- Percentage of critical data stores with classification, appropriate access controls, recovery copies and tested restoration.
- Number of material scenarios above the organization’s stated risk appetite, with residual risk by business unit, geography or critical service.
“Two revenue-critical systems remain outside authenticated inventory and could interrupt order processing for three days” is more decision-useful than “98% asset visibility.” CISA’s performance goals and asset-visibility guidance provide practical baseline outcomes, but they are not proof that all material risk has been reduced (CISA Cybersecurity Performance Goals; CISA asset-visibility directive).
2. Vulnerability and attack-path exposure
Raw CVE totals conceal exploitability, business importance, age and compensating controls. Report weaknesses that create a plausible route to a critical service.
- Known exploited vulnerabilities affecting critical systems.
- Median and oldest age of critical vulnerabilities, plus the percentage remediated within the approved service level.
- Percentage of critical assets covered by authenticated scanning.
- Internet-facing critical systems with unsupported software, unresolved exploitable weaknesses, legacy authentication or unnecessary exposed services.
- Unresolved paths from internet-facing assets to critical systems, compromised identities to sensitive data, or suppliers to production environments.
- Exceptions with a named owner, expiration date, compensating control and documented residual risk.
Use a business statement: “Three customer-facing systems have exploitable weaknesses outside the patch window; two are isolated, one has accepted residual risk, and replacement funding is requested by Q4.”
3. Identity and privileged-access risk
Multifactor authentication coverage is not enough unless the board can see what it covers.
- Percentage of privileged accounts protected by phishing-resistant MFA.
- Standing privileged accounts, dormant or orphaned accounts, shared accounts and service accounts.
- Critical applications covered by single sign-on, strong MFA, joiner-mover-leaver controls and privileged-access management.
- Median time to remove access after termination.
- High-risk access exceptions, their age and overdue reviews.
- Emergency or break-glass accounts, including last-use and review status.
Ask which critical systems remain reachable through credentials that would not resist phishing, and when those pathways will be retired.
Rank #2
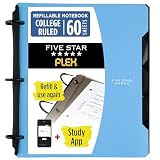
- Sheets stay put! Flexible Rings won't break or misalign.
- Acts like a notebook. Plastic cover folds back over the rings to lie flat like a notebook cover.
- Works like a binder. TechLock rings allow you to easily add or remove sheets. 1 in. rings hold up to 200 sheets.
- NoteBinder comes prefilled with 60 college ruled sheets. Also includes 2 NotePocket dividers to store loose sheets and 3 NoteProtector dividers to protect important papers.
- Customize the cover by sliding in your own photo or agenda for a personal touch. Durable clearview cover also protects your contents from damage.
4. Detection, response and incident readiness
Response measures should show whether a serious event can be recognized and contained, not merely how busy the security team is.
- Median time to detect and median time from detection to containment for high-severity incidents.
- Percentage of critical systems sending useful logs to monitored platforms.
- High-severity alerts with a documented playbook, assigned owner and tested escalation path.
- Incidents that bypassed preventive controls or remained undetected beyond approved tolerance.
- Material scenarios exercised in the past 12 months.
- Time required to notify executives, the board, counsel, regulators, customers or partners when applicable.
- Open lessons-learned actions and corrective actions completed by their due dates.
NIST SP 800-61 Rev. 3, published in April 2025, links incident response with CSF 2.0 risk management (NIST SP 800-61 Rev. 3). Define each time metric consistently: changes in logging coverage, severity rules or ticketing can make an apparent improvement meaningless.
5. Recovery and operational resilience
Detection does not prevent prolonged damage if critical services cannot be restored.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →- Critical services with tested recovery plans.
- Backups meeting recovery-point, recovery-time, immutability and isolation requirements.
- Successful restoration rate, actual recovery time versus objective, and actual data loss versus objective.
- Critical services dependent on one supplier, administrator, cloud region or untested credential.
- Resilience exercises that exposed material gaps, with age and severity of unresolved issues.
- Estimated revenue, customer, safety or regulatory impact for the leading disruption scenarios.
“Backup success rate” is weak. “The payment platform restored in five hours against a four-hour objective, using a manual key-recovery procedure known by two employees” exposes the decision.
6. Governance, accountability and investment
- Top risks with an executive owner, funded treatment plan, target date and residual-risk decision.
- Overdue high-risk actions, expired exceptions and repeat findings by business unit or control domain.
- Budget allocation to risk reduction, resilience, compliance, technology replacement, personnel and operations.
- Major initiatives delayed by staffing, architecture, vendors, funding or business-owner resistance.
- CISO access to the board or committee and frequency of independent assessments.
Budget size, headcount, tool count and compliance status are inputs, not evidence that risk is within tolerance.
Rank #3

- Sheets stay put! Flexible Rings won't break or misalign.
- Acts like a notebook. Plastic cover folds back over the rings to lie flat like a notebook cover.
- Works like a binder. TechLock rings allow you to easily add or remove sheets. 1 in. rings hold up to 200 sheets.
- NoteBinder comes prefilled with 60 college ruled sheets. Also includes 2 NotePocket dividers to store loose sheets and 3 NoteProtector dividers to protect important papers.
- Durable cover also protects your contents from damage.
Metrics boards should demote
| Metric | Why it misleads | Better board question |
|---|---|---|
| Attacks blocked | May reflect more attacks, exposed services, sensors or changed rules. | Which material attack paths remain open? |
| Total vulnerabilities | Ignores exploitability, asset criticality, age and controls. | Which known exploited weaknesses affect critical services? |
| External security rating | Methodologies may be opaque and do not measure internal resilience. | What evidence supports the rating and what does it exclude? |
| Compliance percentage | Shows selected requirements, not performance under attack. | Which controls failed testing or lack coverage? |
| Training completion | Measures participation, not safer behavior. | Are susceptibility, reporting and risky workflows improving? |
| Incident count | Can fall because of underreporting or weaker visibility. | Did definitions, monitoring coverage or classification change? |
“All critical patches are current” still requires the definition of critical, coverage of internet-facing assets, treatment of known exploited vulnerabilities, unavailable systems and the oldest exception.
How to select and present a metric
Before adding a measure, answer these questions:
- What decision could it change?
- Which business service, asset, dependency or scenario does it describe?
- What is the denominator and what is excluded?
- Can the result be reproduced and audited?
- Can it be trended under stable definitions?
- What action occurs at each threshold?
- Who owns improvement?
- Could the number improve while real risk worsens?
- Does it show scope, severity, age and exceptions?
- Can a nontechnical director understand the consequence?
NIST SP 800-55v2 is useful for selecting, defining, collecting and using measures (NIST measurement program).
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsMetric-card template
- Metric: Percentage of critical services with tested recovery.
- Current/prior/target: 82% / 74% / 95% by December 31, 2026.
- Scope: 39 of 47 critical services.
- Trend: Improving.
- Business implication: Eight services may miss the approved recovery objective during ransomware.
- Owner: COO and CIO.
- Exception: Two services rely on a supplier with incomplete recovery evidence.
- Board action: Approve replacement funding or accept residual risk by a stated date.
Every card should include reporting period, data source, severity model, confidence or data-quality rating, scope exclusions and methodology changes. Thresholds should be tied to risk appetite—for example, any critical service without a tested recovery plan after its due date triggers escalation.
A practical dashboard layout
Page 1: Executive risk summary
Show overall direction, the top three scenarios, residual risk versus appetite, one business consequence for each, decisions or funding requested and material changes since the prior report.
Page 2: Risk exposure
Show critical-service coverage, attack-path exposure, identity exceptions, supplier concentration, unsupported technology and high-risk exceptions by age and owner.
Rank #4

- Heavy-Duty binders have a DuraHinge design that's stronger, lasts longer and resists tearing, while the DuraEdge feature makes the sides and top more pliable to resist splitting
- Deep texture film offers a smoother finish and features a linen pattern for high-quality look and feel
- Nonstick, archival-safe material means binders won't lift ink or toner off printed pages
- Wide front and back binder panels fully cover standard dividers and sheet protectors
- Organize and secure paper with four stacked pockets
Page 3: Control and resilience effectiveness
Show remediation performance, detection and containment, critical logging, recovery tests, restoration results, exercises and repeat failures.
Free tools Windows power users keep installed
One-click scans. No signup required.
Page 4: Accountability and investment
Show overdue actions, risk acceptance, budget versus plan, milestones, capability constraints and independent-assurance findings. Keep detailed definitions and methodology in an appendix.
Reporting cadence and escalation
| Cadence | Use |
|---|---|
| Monthly management | Vulnerability aging, patching, identity exceptions, alerts, control failures, tickets and supplier alerts. |
| Quarterly board or committee | Top risks, appetite breaches, critical-service exposure, resilience tests, material exceptions, funding and decisions. |
| Immediate escalation | Material incident, impaired critical service, relevant major supplier incident, tolerance breach, missed legal or contractual deadline, failed critical control or risk-changing program delay. |
Questions directors should ask
- Which three scenarios could most affect revenue, operations, safety, customers or regulatory standing?
- What changed in those scenarios since the last report?
- Which critical assets or services remain outside reliable inventory?
- Which known exploited vulnerabilities affect critical systems?
- Which exceptions exceed approved age or tolerance?
- What percentage of privileged access is phishing-resistant?
- Can the most important services be restored within their stated objectives?
- When was the last realistic recovery exercise, and what failed?
- Which supplier or fourth party could interrupt a critical service?
- Which metrics rely on incomplete or low-confidence data?
- Where might the dashboard improve while actual risk worsens?
- What decision, funding or risk acceptance is required?
- How independently has management’s assessment been tested?
- What would cause notification between scheduled meetings?
Special cases boards should handle explicitly
Small organizations
When incident-frequency or time-to-detect data is too sparse, use scenario measures: identified critical services, protected administrator accounts, completed recovery tests, understood supplier dependencies, exercised incident roles and actively owned exceptions.
Cloud-native companies
Add production identity paths, cloud-account separation, exposed storage and services, infrastructure-as-code coverage, secrets exposure, control-plane recovery and managed-service dependencies.
Operational technology and safety-critical environments
Where patching is constrained by safety, availability, certification or vendors, report segmentation, monitoring, maintenance windows, compensating controls and replacement plans.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Best Value

- Five Star Advanced 5 Subject College Ruled Notebook
- LASTS ALL YEAR. GUARANTEED!*
- Includes 1 movable plastic divider; place anywhere in notebook to organize your work.
- 200 Sheets
Mergers and acquisitions
Separate inherited risk, unintegrated identities, shared trust relationships, unsupported systems, unassessed suppliers and gaps in response or recovery coverage.
Third parties
Prioritize suppliers by service criticality, data access, connectivity, concentration, substitutability, recovery dependency, notification obligations and evidence quality—not vendor count alone.
Governance and U.S. disclosure considerations
For U.S. public companies subject to applicable Exchange Act reporting requirements, SEC rules address periodic disclosure of cybersecurity risk-management processes, management’s role and board oversight, along with current disclosure of material cybersecurity incidents (SEC cybersecurity disclosure rule; SEC compliance guide). SEC materiality is fact-specific and concerns what a reasonable investor would consider important; it is not a fixed dollar threshold (SEC Disclosure Guidance Topic No. 2). Coordinate board reporting with legal, finance, investor relations and disclosure controls. A dashboard is not a substitute for fact-specific disclosure analysis or legal advice.
Choosing implementation tools
| Approach | Best fit | Trade-off |
|---|---|---|
| Spreadsheet and manual reporting | Smaller organizations with disciplined owners and stable data. | Transparent and inexpensive, but fragile at scale and prone to version-control problems. |
| Vanta | Compliance automation plus risk registers, treatment plans and reporting. | Personalized pricing at Vanta pricing; may be light for complex enterprise-risk workflows. See Vanta Risk. |
| Drata | Organizations expanding from compliance into GRC and third-party risk. | Personalized pricing; a narrow dashboard need may not justify broad evidence functionality (Drata plans). |
| Secureframe | Compliance, infrastructure monitoring, risk and trust-center requirements. | Quote-based; compliance automation is not a complete business-risk model (Secureframe pricing). |
| UpGuard | Supplier and ecosystem risk. | Standard Vendor Risk plan listed at $1,750 per month billed annually for monitoring 50 vendors; higher tiers require sales. It does not replace internal identity, recovery or operations governance (UpGuard pricing; UpGuard reporting). |
| Board Cybersecurity | Board-oriented external monitoring, benchmarking and briefing. | Professional is $200 per month billed annually and Business $500 per month billed annually; Enterprise is custom. Verify beta labels, data provenance, integrations and internal telemetry coverage (Board Cybersecurity pricing). |
| ServiceNow Integrated Risk Management | Large enterprises needing integrated risk, continuity, third-party workflows and operational resilience. | Enterprise implementation and sales engagement; potentially excessive for a quarterly dashboard (ServiceNow GRC). |
Evaluate any product on business-service linkage, inherent/control/residual-risk separation, denominators, exceptions, historical snapshots, integrations, role-based access, explainable ratings, exportability and total implementation cost. If the underlying data is unreliable, buying a prettier dashboard will not fix the measurement problem.
Bottom line
The strongest board cybersecurity metric is not the most precise technical number. It is the measure that makes business exposure visible, assigns responsibility, shows whether resilience works and forces a timely decision—or reveals that no decision has been made.
Frequently Asked Questions
How many cybersecurity metrics should a board review?
Use a compact set covering critical exposure, attack-path risk, identity, response, recovery and accountability. The right number depends on complexity; each metric must have a defined denominator, owner, threshold and decision.
Is NIST CSF 2.0 a cybersecurity scorecard or certification?
No. NIST CSF 2.0 is a framework for managing cybersecurity risk, including governance. It does not provide a universal percentage score or guarantee against compromise.
Do SEC cybersecurity rules apply to every organization?
No. The cited SEC requirements apply to U.S. public companies subject to applicable Exchange Act reporting obligations. Other organizations should obtain fact-specific legal guidance.
Recommended Free Tools
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




