Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errorsShort answer: Dell confirmed in May 2024 that a portal incident exposed customer names, physical addresses and purchase-related information. The often-repeated figure of 49 million records came from a threat actor, not from a Dell-confirmed breach total. Dell said the affected portal data did not include email addresses, telephone numbers, payment information or other highly sensitive information.
The alleged use of a Dell partner-portal API was described by the attacker and reported by security outlets, but Dell has not published a technical postmortem confirming every detail of that account.
What Dell actually confirmed
Dell’s customer notice described an incident involving a portal and a database containing information associated with purchases. The notice listed these potentially affected fields:
- Customer name
- Physical address
- Dell hardware information
- Order information
- Service tag
- Item description
- Order date
- Related warranty information
Dell said the incident did not involve email addresses, telephone numbers, payment or financial information, or other “highly sensitive” customer information. Dell said it activated incident-response procedures, contained the incident, notified law enforcement and hired a third-party forensics firm. Dell’s customer notification does not state how many customers were affected.
#1 Best Overall

- Vibrant Visuals: Enjoy vivid, accurate colors with up to 300 nits brightness on a spacious 15" display featuring a sleek 3‑sided narrow bezel.
- AI Productivity: Boost efficiency with Intel Core Ultra processors and NPU‑powered AI features designed to keep multitasking smooth and responsive.
- Smarter Shortcuts: Use the dedicated Copilot key for instant access to your AI assistant, helping you organize, search, and work faster every day.
- Eye Comfort: Dell ComfortView reduces blue‑light emissions to help keep your eyes comfortable during extended viewing.
- Ergonomic Angle: Lifted hinges enhance typing comfort and support better airflow, helping your system run smoothly.
Where the “49 million” figure came from
On April 29, 2024, a threat actor using the name Menelik advertised a Dell-related database on a cybercrime forum. The seller claimed it contained approximately 49 million records covering Dell systems purchased between 2017 and 2024. The fields described in the advertisement broadly matched information Dell later said had been accessed.
TechCrunch reported the advertisement and Dell’s subsequent disclosure, but Dell did not publicly validate the number. The accurate description is therefore that Dell confirmed a customer-data incident, while a threat actor claimed the dataset contained about 49 million records. It is not accurate to say Dell confirmed that 49 million customers were stolen. TechCrunch’s report documents the public account.
Rank #2
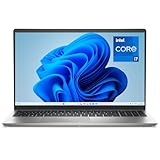
- Effortlessly chic. Always efficient. Finish your to-do list in no time with the Dell 15, built for everyday computing with 13th Gen Intel Core i7-1355U processor
- Designed for easy learning: Energy-efficient batteries and Express Charge support extend your focus and productivity.
- Stay connected to what you love: Spend more screen time on the things you enjoy with Dell ComfortView software that helps reduce harmful blue light emissions to keep your eyes comfortable over extended viewing times.
- Type with ease: Write and calculate quickly with roomy keypads, separate numeric keypad and calculator hotkey.
- Ergonomic support: Keep your wrists comfortable with lifted hinges that provide an ergonomic typing angle.
Was this an API breach?
The API explanation comes from the attacker’s account and secondary reporting, rather than a public Dell forensic report. BleepingComputer reported that the actor said they:
- Registered fake companies as Dell partners or resellers.
- Used access to a partner portal.
- Guessed or brute-forced Dell service-tag values.
- Collected the records returned by the portal’s API.
Kaspersky’s incident summary attributed to the actor a scraping rate of approximately 5,000 requests per minute for nearly three weeks. That rate and duration remain unverified claims, not established Dell findings. Kaspersky’s summary and BleepingComputer’s report describe the alleged method.
Rank #3

- 256 GB SSD of storage.
- Multitasking is easy with 16GB of RAM
- Equipped with a blazing fast Core i5 2.00 GHz processor.
At a high level, the reported weaknesses would involve several control failures: weak vetting of partner registrations, predictable or enumerable service-tag identifiers, insufficient record-level authorization, inadequate rate limiting, poor detection of sustained automated requests and an endpoint returning more data than necessary. No operational endpoint, request format or exploitation code has been publicly established in the sources cited here.
What “49 million records” does—and does not—mean
A record is not necessarily one unique, current customer. A large historical database can contain repeat orders, duplicate entries, business addresses or several purchases linked to the same person or organization. “49 million customers” and “49 million records” are therefore not interchangeable.
Rank #4
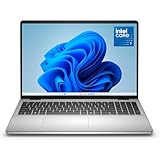
- Edge-to-edge clarity: Enjoy crisp, expansive visuals on a 16" screen with up to FHD+ and a 16:10 aspect ratio—delivering a wide, immersive viewing experience.
- All-day comfort: Dell ComfortView Plus helps reduce harmful blue light emissions while preserving true-to-life color, keeping your eyes comfortable even during prolonged screen time.
- Ready for business: Flip between effortless productivity and captivating entertainment on a large, immersive screen powered by Intel Core 7-150U processor and graphics.
- Built for virtual connection: Bring your connections to life with an up-to FHD camera, designed with wide dynamic range and temporal noise reduction to deliver crisp, sharp images, no matter the lighting conditions.
- Adaptive thermals: Built-in technology allows your PC to sense when it's on a stable surface and adjusts its power and thermals to run more efficiently.
The public record does not establish:
- The number of unique individuals or organizations represented.
- Whether the advertised database was complete, authentic or altered.
- Whether every record belonged to a Dell customer during the claimed 2017–2024 period.
- Whether Dell independently confirmed the seller’s scraping method or volume.
Dell’s notification also did not publish a total affected-customer count.
A separate Dell portal report should not be merged with this incident
On May 14, 2024, separate reporting described another Dell portal containing customer-support-ticket information, allegedly including names, phone numbers and email addresses. That report concerned different data and should not automatically be treated as part of the 49-million-record dataset. TechCrunch reported both the separate portal allegation and Ireland’s regulatory notification.
Best Value

- Effortlessly chic. Always efficient. Finish your to-do list in no time with the Dell 15, built for everyday computing with Intel processors.
- Designed for easy learning: Energy-efficient batteries and Express Charge support extend your focus and productivity.
- Stay connected to what you love: Spend more screen time on the things you enjoy with Dell ComfortView software that helps reduce harmful blue light emissions to keep your eyes comfortable over extended viewing times.
- Type with ease: Write and calculate quickly with roomy keypads, separate numeric keypad and calculator hotkey.
- Ergonomic support: Keep your wrists comfortable with lifted hinges that provide an ergonomic typing angle.
Ireland’s Data Protection Commission confirmed on May 16 that it had received a breach notification concerning Dell and was assessing it. The cited report does not provide a final regulatory finding or penalty.
A 2025 Dell “Solution Center” incident was another separate event, not an update to the 2024 partner-portal matter. TechRadar described that later incident.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.What risks remain for customers?
The disclosed fields are less immediately dangerous than passwords or payment cards, but they can make impersonation much more convincing.
- Targeted tech-support scams: A caller who knows your service tag, device description or warranty status may sound like legitimate Dell support.
- Warranty and repair fraud: A scammer can invent a warranty renewal, replacement or repair problem and request money or remote access.
- Social engineering: A physical address combined with order dates and hardware details can help an attacker persuade you or an employee to reveal more information.
- Phishing and phone impersonation: Even without an email address in this portal, exposed purchase details can be combined with information obtained elsewhere.
- Business-location exposure: A business address can reveal where particular equipment or employees are located, which may matter to targeted attackers.
A service tag is useful intelligence for a scammer, but it is not equivalent to a password. Dell’s notice says the affected portal did not include payment information, email addresses, telephone numbers or highly sensitive data, which limits—but does not eliminate—identity and fraud risk.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallWhat Dell customers should do
- Verify unexpected contacts independently. Do not trust a phone number, link or callback instruction supplied by an unsolicited caller. Type Dell’s address manually or use a bookmark to reach official support.
- Refuse remote access and secrets. Do not provide passwords, one-time codes, payment details, identity documents or remote-control access to an inbound caller claiming to be Dell.
- Check your records. Review Dell account activity, order history and warranty information for changes you did not make.
- Change reused passwords. Dell said the disclosed incident did not include account passwords or email addresses, but any password reused on other services should be replaced there and protected with multifactor authentication where available.
- Report suspicious activity. Dell listed [email protected] as a security contact. Preserve messages, caller details and payment requests when reporting a scam.
- Consider credit protections proportionately. A credit freeze or fraud alert may make sense if you have separate evidence that financial or identity data was exposed. The fields Dell disclosed by themselves do not establish exposure of Social Security numbers, bank details or payment cards.
Timeline and evidence status
| Date | What was reported | Evidence status |
|---|---|---|
| April 29, 2024 | A Dell-related database was advertised on a hacking forum. | The approximately 49-million figure came from the threat actor. |
| May 9, 2024 | Dell notified customers about a portal incident involving purchase-related information. | Dell confirmed the incident and listed exposed and excluded fields; it did not state a total. |
| May 10, 2024 | Reporting described fake-company registration and partner-portal API abuse. | Technical details were attributed to the attacker. |
| May 14, 2024 | A separate report described support-ticket data, including phone numbers and email addresses. | Treat as a distinct portal exposure unless primary evidence links the datasets. |
| May 16, 2024 | Ireland’s Data Protection Commission confirmed receiving a Dell breach notification. | The cited report does not disclose final findings. |
| 2017–2024 | The advertised dataset was said to cover systems purchased in this period. | Seller’s description, not a Dell-confirmed scope. |
| Approximately 5,000 requests per minute for nearly three weeks | Scraping volume and duration cited in Kaspersky’s incident overview. | Attacker claim reported by a secondary source, not confirmed by Dell. |
What remains unknown
- The exact number of unique affected people and organizations.
- The duration and start date of unauthorized access.
- Whether Dell independently confirmed the alleged API weakness and scraping volume.
- Whether the advertised database was complete, authentic or modified.
- Whether any additional fields existed outside the disclosed portal dataset.
- Whether regulators ultimately issued findings or penalties.
The Bottom Line
Bottom line: The Dell incident was real, but “49 million records” remains a threat-actor claim rather than a confirmed Dell total. The publicly disclosed portal data consisted of names, addresses and purchase, hardware and warranty details—not passwords, payment information, email addresses or phone numbers. The most practical response is to expect more convincing Dell-support impersonation and verify every unsolicited contact through an official channel.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




