The “dozens of banks” warning most likely refers to DroidBot, an Android banking trojan publicly reported in December 2024—not a newly confirmed attack in August 2026. Researchers said it had been active since at least June 2024 and targeted 77 banking, cryptocurrency, and national-organization applications or entities; that figure does not mean 77 banks were breached. Available reporting does not establish that the same DroidBot campaign is currently active.
What DroidBot is—and what the headline gets wrong
DroidBot is more accurately described as an Android remote-access trojan (RAT) with banking-trojan capabilities, rather than simply a “virus.” It infects a customer’s phone and can abuse access to financial apps; the reporting does not describe a breach of the banks’ internal networks. SecurityWeek’s December 2024 report said researchers had observed activity since at least June 2024 and identified 77 targets spanning banking apps, cryptocurrency exchanges, and national organizations.
Gen Digital reported that DroidBot was offered as malware-as-a-service, with up to 17 affiliates. That model can make a tool available to multiple operators, but it does not establish who they are or that every affiliate used every capability. Gen Digital’s Q4 2024 threat report provides that service-model context.
The distinction matters for personal finances: criminals may steal credentials or manipulate a customer’s active phone session without penetrating a bank’s systems. Account takeover, a bank breach, phishing, and a victim being tricked into approving a payment are different events, even if they can lead to similar losses.
Free tools Windows power users keep installed
One-click scans. No signup required.
#1 Best Overall
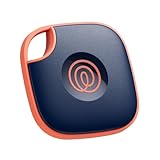
- THE EVERYTHING TRACKER: Protect lost or stolen stuff and make family life easier. Attach to everyday things like keys, water bottles, or bags
- STAY SAFE WITH SOS: Discreetly trigger an SOS alert to your loved ones in unsafe situations
- FIND YOUR THINGS: Ring your misplaced Tile, or track it down in the free app
- FIND YOUR PHONE: Phone hiding under a cushion? Use your Tile to make it ring — even when silenced
- USE WITH LIFE360: Add your Tiles to Life360 — a top family connection and safety app – to see everything and everyone on the same map
Is DroidBot still attacking people in 2026?
The confirmed timeline in the cited DroidBot reporting is historical: activity was observed from at least mid-2024 and publicly reported in December 2024. The available sources do not verify that DroidBot’s command-and-control infrastructure remains active, that the same campaign is spreading now, or that it is currently targeting U.S. bank customers.
Banking trojans remain a current threat category, but reports about other malware should not be treated as proof that DroidBot is active. For example, a July 2026 report described Ousaban, a separate trojan targeting Windows users and more than two dozen banks in Spain and Portugal: The Hacker News report on Ousaban. Barracuda also discussed banking-trojan account-takeover fraud in 2026, without establishing that DroidBot was responsible: Barracuda’s 2026 overview.
DroidBot reporting described activity concentrated mainly in France, Italy, Spain, Portugal, Turkey, and the United Kingdom, with possible expansion to Latin America. The cited reporting does not establish U.S. banks among its confirmed targets. Its techniques are not inherently limited to Europe, however, so Android users elsewhere should still take suspicious app installations and permission requests seriously.
Rank #2

- Works with Apple Find My: Just use the pre-installed Find My app and add SmartTrack Link to the Items tab. You can then locate it anywhere in the world using Apple's network of millions of devices. Note: Apple Find My features only work if used with an iOS, iPadOS, or macOS device.
- Find Your Phone in Silent Mode: Avoid tearing up your apartment searching for your phone. With just a double tap, your phone rings—even in silent mode.
- Free Left-Behind Alerts: Avoid losing your belongings in the first place with instant left-behind alerts via the eufy Security app—with no added fee.
- Always Linked to Your Item: If something's lost, you're always connected via Link's QR code. A person who finds your item can scan and see only the contact information you share.
- Share with Friends and Family: With the eufy Security app you can let others know the location of your items too.
How infection can happen
The reported delivery methods included apps disguised as banking or security tools, Google-related services, or other legitimate-looking utilities. The risk usually involves installing an untrusted app, such as a sideloaded APK, and granting it powerful access—not simply visiting a bank website. One reported attack chain looks like this:
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Fix the driver behind crashes, sound loss and screen glitches3Clear out junk files and repair common Windows errors- A person encounters a fake app, update notice, or security prompt.
- They install the app, sometimes from outside Google Play.
- The app asks for Accessibility access or other sensitive permissions.
- With access, the malware may observe the screen, interact with apps, intercept messages, or display a fake login screen.
- Operators may use captured information or control of the phone to attempt account access or transactions.
Be especially wary of an app or message that urges you to install an update outside Google Play, accept an APK through messaging or social media, disable Play Protect, or grant Accessibility access without a clear reason. An app asking to read SMS, control the screen, or appear over other apps deserves careful scrutiny.
What the malware can do to a banking session
SecurityWeek and other reporting describe capabilities including overlays that imitate legitimate banking screens, keystroke capture, user-interface monitoring, screenshots, SMS interception, remote control, and simulated taps. These are reported capabilities, not proof that every sample used every feature. Verimatrix’s threat roundup also summarizes the reported technical behavior.
Rank #3

- REDESIGNED TO DO MORE: The redesigned Galaxy SmartTag2 is made so you can keep calm and keep track¹; Its design makes it easy for you to tag and carry your belongings
- EASY TO USE: It's IP67-rated water- and dust-resistant², activates your compatible IoT devices³ and stays powered for up to 500 days⁴ or even up to 40% more on Power Saving Mode⁵
- RELAX, YOU'VE GOT IT TAGGED: Simply register a new Galaxy SmartTag2 and get started right away with SmartThings Find; With its intuitive tracking experience, you now have a way to keep track of things you love right in the palm of your hand¹
- SEARCH NEAR WHEN IT'S NOT FAR: Lose something? Switch on Search Nearby⁶ and get instructions to your item's location via Compass View⁷; If you still don't see it, just ring your Galaxy SmartTag2 to have it send out an audible signal
- TAGGED & TRENDY: Cover your Galaxy SmartTag2 with a colorful Silicone Case for protection and a smooth touch – or a Rugged Case with a non-slip pattern on the side and additional bumper on the bottom⁸; Both have a carabiner ring attachment
- Credential theft: A fake login screen or keylogging may expose a username, password, PIN, or other information.
- Authentication-code theft: If the malware can read SMS, it may capture a texted one-time code.
- On-device fraud: If the phone is under remote control or the banking session is already authenticated, an operator may try to make actions through the victim’s device.
SMS-based two-factor authentication is not a guarantee if the same compromised phone receives the code. An authenticator app, passkey, hardware key, transaction signing, or confirmation on a separate trusted device can reduce some risks, but no method should be treated as a guarantee after a device is compromised. Ask your bank what authentication and transaction controls it supports.
Who should be most alert?
- Android users who install apps from links, APK files, messaging apps, or unofficial app stores.
- People who grant Accessibility, SMS, notification, screen-overlay, or device-administrator access without checking why it is needed.
- Customers who use the same phone for banking, email, and SMS authentication.
- Small-business owners who approve wires or ACH transfers on a phone without a separate review or approval step.
- Cryptocurrency users, since cryptocurrency exchanges were among the reported target categories.
For businesses, separate banking devices for high-value accounts, least-privilege mobile administration, dual approval for large transfers, and out-of-band confirmation of new payees can limit reliance on one potentially compromised phone.
Warning signs—and what they can and cannot tell you
Possible warning signs include unexpected Accessibility prompts, unfamiliar apps with generic names or blank icons, banking apps opening or closing unexpectedly, overlays or fake security warnings, unexplained changes to SMS messages, unusual battery or data use, and logins or transactions you do not recognize. None of these signs alone proves DroidBot infection; they are reasons to investigate, not a diagnosis.
Rank #4

- A FIDO security key with PUF technology provides a unique, hardware-rooted trust anchor that resists tampering and cyber attacks, offering stronger security than conventional designs.
- FIDO2 Certified Protection – Enjoy phishing-resistant security with FIDO2 certification, ensuring top-tier account safety across Windows, macOS, Linux, iOS iOS, Android and more.
- Easy to use & Portable – Designed with a compact USB-C interface, Clife key fits easily on your keychain for secure access anywhere. Simply plug in and authenticate with ease.
- Universal Compatibility – Works seamlessly with hundreds of FIDO2/U2F compliant services, including popular cloud, email, and social platforms.
- Backup recommended – To ensure continuous access, register a backup Clife security key as a spare in case your primary key is lost.
A security scan that finds nothing also does not prove the phone was never compromised. Malware may be obfuscated, removed after information was stolen, or identified under another name. If credentials or transactions may have been exposed, take the account-protection steps below even if a scan is clean.
What to do if you installed a suspicious app or see an unknown transaction
- Stop using the suspected phone for financial activity. Do not use it to log in, approve transfers, or change passwords.
- Contact your bank from a clean device. Use the official app or website on that device, or the phone number printed on your bank card—not a number in a suspicious pop-up. Ask the bank to review logins and transactions, restrict transfers or mobile access if appropriate, replace compromised credentials, and add alerts or verification.
- Secure accounts from the clean device. Change banking and email passwords, revoke unfamiliar sessions and trusted devices, and review recovery details and recent payees.
- Contact your mobile carrier if SMS or SIM abuse is possible. Ask it to check for unauthorized account or SIM changes.
- Preserve evidence. Record the app name and installation source, keep suspicious messages and transaction alerts, and note dates, times, and screenshots where safe to do so.
- Report financial loss promptly. In the U.S., consumers can file with the FBI Internet Crime Complaint Center, use the FTC’s identity-theft guidance, or submit a complaint to the Consumer Financial Protection Bureau.
If a bank calls a transfer “authorized,” explain that you did not knowingly initiate it and ask for a fraud investigation. A transaction can be made through a victim’s device without the victim understanding or intending the action. Keep device and transaction evidence and follow the bank’s reporting process quickly.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Check and clean an Android phone
Android menu names vary by manufacturer and version, so use Settings search if the labels below do not match your phone. Do not delay contacting the bank while troubleshooting.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Best Value
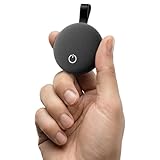
- Works with iOS & Android Systems - Compatible with Apple Find My and Android Find Hub, this Bluetooth tracker lets you locate items directly from your phone. Easy pairing and reliable connection let you start tracking in minutes, no tech skills required (Note: Cannot pair with iOS and Android devices simultaneously.)
- Find Items Fast with Loud Ringing - Misplaced something nearby? Tap your phone to trigger a loud 80dB ring and locate your items within a 40m range. No guessing, no searching, just quick results when you are in a hurry or heading out the door
- Certified Security with Full Privacy Protection - Built with Apple MFi and Google GMS certification, this item tracker follows strict security standards. Location data is encrypted and anonymized, giving you reliable tracking without sacrificing personal privacy
- Premium Fabric Finish, Built for Daily Use - Featuring a refined fabric-textured exterior, this tracker combines durability with style. IP65 waterproof and drop resistant, it is designed to handle everyday splashes, bumps, and outdoor use with ease
- Share Access with People You Trust - Easily share your tracker with family or friends. iOS supports up to 5 shared users, Android supports up to 10. Everyone can help locate shared items while you stay in full control of permissions
- In Settings, open Accessibility and review installed services. Turn off access for anything unfamiliar or unnecessary.
- In Settings, review Apps for recently installed or unknown apps. Check sensitive access such as notification access, device-admin apps, VPNs, SMS permissions, and “display over other apps.” Remove unfamiliar apps where possible.
- Check Google Play Protect and run its scan. Google’s current guidance is at Google Play Protect help.
- Install pending Android system and app updates, and install future apps only from sources you trust.
- If suspicious behavior persists or you cannot remove the app, consider backing up essential personal files and performing a factory reset. Do not restore unknown APK files or questionable backups.
A factory reset addresses the phone, not stolen credentials, exposed account information, or active banking sessions. Complete the bank and account steps even if the reset appears to resolve the device symptoms.
Common mistakes to avoid
- Do not install an APK sent by an unknown person or follow a pop-up’s instructions to disable Play Protect.
- Do not grant Accessibility access just because an app claims it is required for security or an update.
- Do not call a number shown in a suspicious warning or use the possibly infected phone to change passwords.
- Do not assume that a successful bank login, a clean scan, or a factory reset by itself means your accounts are safe.
- Do not spend time trying multiple “cleaner” apps before notifying the bank about suspicious transactions.
Optional protection tools
Google Play Protect is a sensible baseline included with Google Play and Android; Google’s instructions explain how to check its status and scan apps: Play Protect help. A third-party mobile-security app may add scanning, web protection, or privacy checks, but it cannot guarantee detection of every RAT or investigate bank fraud. No current product price is established here; pricing and features can vary by country and subscription. A scanner is not a substitute for contacting the bank, changing exposed credentials from a clean device, and reviewing transactions.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




