
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallShort answer: A cyberattack detected by Stryker on March 11, 2026, disrupted systems used for electronic ordering, manufacturing coordination and shipping. An Iran-linked group called Handala claimed responsibility, but that attribution has not been independently proven as an Iranian government operation. Stryker said its medical products remained safe to use and reported no evidence that customer, supplier or partner systems were accessed.
What happened to Stryker?
Stryker disclosed a cybersecurity incident affecting its internal Microsoft corporate environment. The disruption affected business processes that connect customer orders with production and logistics, including order processing, manufacturing workflows and shipping.
As an Amazon Associate I earn from qualifying purchases.
This was not publicly described as a universal factory shutdown, a takeover of medical devices or a confirmed breach of hospital networks. The evidence instead points to a corporate-IT incident with substantial operational consequences: manufacturing and shipping could continue in some locations or through workarounds, but digital systems supporting those activities were disrupted.
Free tools Windows power users keep installed
One-click scans. No signup required.
Stryker said it used manual ordering, direct communication with sales representatives and distributors, additional shifts and other continuity measures while systems were restored. Some patient-specific cases were rescheduled because of shipping delays.
#1 Best Overall

- Home Security Systems
Timeline of the Stryker cyberattack
| Date | What was reported |
|---|---|
| March 11, 2026 | Stryker identified a cybersecurity incident affecting certain information systems and its internal Microsoft environment. See Stryker’s March 11 Form 8-K. |
| March 12 | The company publicly acknowledged disruption to order processing, manufacturing and shipping. It also filed a regulatory update in a March 12 Form 8-K. |
| March 12 onward | Handala claimed responsibility. Reuters reported that the group described the attack as retaliation for a strike on a girls’ school in Minab, southern Iran. |
| March 15–19 | Stryker said the incident had been contained and that it was prioritizing restoration of customer-facing, ordering and shipping systems. |
| March 19 | Stryker said some patient-specific cases had been rescheduled because of shipping delays. |
| March 23 | Stryker disclosed that investigators working with Palo Alto Networks Unit 42 had identified a malicious file used to run commands and conceal activity. The company said the file was not capable of spreading inside or outside its environment. Stryker also filed a March 23 Form 8-K. |
| March 26 | Reuters reported that manufacturing had been mostly restored and operations were improving toward full capacity. |
“Contained” and “recovered” are different milestones. Containment generally means the company believes the attacker’s access or spread has been stopped. It does not necessarily mean that every system, order, plant or backlog has returned to normal.
Was this ransomware?
Not according to Stryker’s public characterization. Early in the investigation, the company said it had found no indication of malware or ransomware. Later, on March 23, it reported finding a malicious file used to execute commands and hide the attacker’s activity.
Those statements are not necessarily contradictory. A malicious file can be part of an intrusion without the incident being a conventional ransomware attack involving encrypted files and a ransom demand. The later disclosure materially expanded the initial account, showing why early descriptions of an incident can change as forensic investigation proceeds.
Recommended Free Tools
Who was behind the attack?
Handala claimed responsibility for the Stryker attack. Outside researchers and security reporting have described Handala as Iran-linked or pro-Iran and have associated the label with Void Manticore, an Iran-linked actor that researchers believe operates under Iran’s Ministry of Intelligence and Security.
The attribution should be understood in stages:
- Confirmed: Stryker suffered a cyberattack and experienced operational disruption.
- Claimed: Handala said it conducted the attack.
- Reported or assessed: Outside researchers connected Handala with an Iran-linked actor or Void Manticore.
- Not established by the cited public record: That the Iranian government directly ordered or conducted this specific operation.
Reuters reported Handala’s stated motive as retaliation for a strike on a girls’ school in Minab. That is the group’s explanation, not a motive independently confirmed by Stryker.
SecurityWeek’s analysis of the incident provides additional attribution context. The Associated Press also placed the event within a broader pattern of Iran-linked cyber activity targeting organizations in the United States and elsewhere.
Rank #2

- APP Control & Highly DIY: Home Security Systems can be remotely controlled via Smart Life or Tuya APP. Additional PGST sensor accessories can be added, supporting custom sensor naming. With remote control and high expandability, it provides comprehensive protection for your property.
- HD Surveillance Camera: This home security system includes one HD WiFi-connectable camera. Paired with motion detectors and door/window sensors, it enables remote visual monitoring of residential security — no subscription or monthly fees required for thecamera.(MicroSD card sold separately;supports up to 256GB)
- Voice Control & Color Screen Display: Supports connection to smart voice assistants, enabling voice control for home security systems to free hands. The main unit's color screen can display system status, weather, and date, and supports 10 international languages.
- Tamper Protection & Multi-alarm: Home Security System features physical tamper-proof design. Unauthorized removal triggers an alarm requiring a security code to disarm, while automatically sendingphone, SMS and APP alerts for constant security monitoring.
- WiFi+4G Connectivity, No Monthly Fees:Home Security System can connect to 2.4GHz WiFi (5G not supported) and can insert a 4G SIM card for phone call and SMS alarm functions. Permanently free to use after activation with no additional charges.
Were Stryker medical devices compromised?
Stryker said its connected and non-connected products were not affected and remained safe to use. The company characterized the incident as confined to its internal Microsoft environment rather than an attack on the safety or functionality of deployed medical products.
Stryker also said that certain cloud and product environments, including AWS- and Google Cloud-hosted services used by Vocera and care.ai, were not affected. It reported no evidence of malicious activity directed at customers, suppliers, vendors or partners.
These are important company findings, but they should not be rewritten as an independent guarantee covering every device or customer environment. The available reporting does not establish that Stryker devices malfunctioned, were remotely controlled or lost their safety controls.
Was patient data stolen?
The available public statements do not establish that patient data was stolen. Stryker said its investigation had not identified evidence that the attacker accessed customer, supplier, vendor or partner systems.
The defensible wording is therefore: Stryker said it had not identified evidence of access to customer or partner systems. That is different from independently proving that no data was accessed or exfiltrated.
Do these 3 things before closing this tab:
1Repair Windows errors before they cause bigger problems2Scan for outdated or missing drivers - takes under a minute3Clear out junk files and repair common Windows errorsHow did the incident affect hospitals and patients?
The documented patient effect was indirect:
- Electronic ordering was disrupted.
- Shipping and delivery were delayed.
- Some patient-specific procedures were rescheduled.
- Hospitals and distributors faced reconciliation work for orders placed before and during the disruption.
- Backlogs could persist even after systems began returning online.
Patient-specific implants are particularly sensitive to interruptions because they require coordination among clinical planning, production, quality processes and delivery schedules. A delay in the corporate systems supporting those steps can affect a procedure even when the device itself is safe and the hospital’s own network has not been breached.
Rank #3

- EASY DIY SETUP—NO TECHNICIAN NEEDED: Install the wireless alarm hub and sensors yourself with simple step-by-step guidance—no wiring, tools, or installation appointment required.
- 3 MONTHS OF 24/7 PROFESSIONAL MONITORING INCLUDED: Get around-the-clock alarm monitoring from trained professionals who can help contact emergency services when needed.
- SELECT INDOOR SECURITY CAMERA: Select the indoor camera to protect the indoor area that matters most to your home.
- DIY SETUP, ONE COVE APP: Install the alarm system and video doorbell with guided instructions, then use the Cove app to manage your security system, receive alerts, and view doorbell video.
- 3 MONTHS OF 24/7 MONITORING: Includes three months of professional monitoring and supports expansion with additional compatible Cove sensors and devices. Continued monitoring requires a paid plan; no long-term contract is required.
The cited sources do not support claims of a nationwide Stryker shortage, widespread device failure or a compromise of hospital clinical networks. Customers seeking product-specific availability were directed to their local Stryker representatives and distributors rather than to a single universal availability table.
Why a corporate-IT attack disrupted manufacturing
The Stryker incident illustrates a major healthcare supply-chain risk: a company does not need to lose control of a medical device for patient care to be affected.
Modern manufacturing depends on shared digital services for identity, scheduling, inventory, quality documentation, order management, production coordination and transportation. If those systems become unavailable or untrusted, physical production may continue while the surrounding workflow slows or stops.
Several failure modes matter:
- Centralized identity dependency: A compromised or unavailable Microsoft environment can block access to multiple business applications at once.
- Manual-workaround risk: Phone, email or paper-based processes can preserve urgent supply but create duplicate orders, reconciliation errors and backlogs.
- Patient-specific vulnerability: Customized products have less flexibility than standardized inventory already held by a hospital.
- Non-ransomware disruption: Attackers can cause serious interruption through command execution, account lockouts, destructive actions or loss of trust in systems without encrypting files.
- Staged recovery: Restoring a production line does not automatically restore ordering, shipping, customer support, data reconciliation or every regional operation.
What remains unknown
The public record cited for this article does not establish:
- How the attackers first gained access.
- Which specific systems they accessed or altered.
- Whether any data was exfiltrated.
- Independent confirmation of the Handala attribution.
- The incident’s total financial impact.
- Whether every backlog was eliminated after manufacturing was mostly restored.
- Whether the malicious file was a custom tool, abuse of a legitimate utility or another type of payload.
- Whether other healthcare manufacturers were targeted in the same campaign.
What hospitals should do after an incident like this
- Confirm alternate contacts. Keep current phone numbers and escalation paths for Stryker representatives, distributors and emergency-ordering teams.
- Separate stocked and patient-specific risk. Review near-term procedures, implant requirements, replenishment levels and substitute-product options.
- Use offline procedures. Maintain tested processes for urgent orders, approvals, inventory checks, receiving and reconciliation when vendor portals are unavailable.
- Check your own environment. A disruption at a supplier does not by itself show that the hospital’s Microsoft environment was breached, but organizations should monitor identity, endpoint and cloud logs for related activity.
- Coordinate communications. Establish who informs clinicians, operating rooms, procurement, distributors and patients if a delivery changes.
What manufacturers should learn
Resilience requires more than endpoint protection. Manufacturers should protect privileged identities with phishing-resistant multifactor authentication and just-in-time access; segment corporate IT from manufacturing and product environments; preserve independent administrative paths; and test whether production, enterprise-resource-planning, logistics and identity systems can be restored in the correct order.
Backups should be isolated from compromised credentials, regularly tested and usable without relying on the same identity infrastructure that may be under attack. Incident-response plans should also cover manual production scheduling, shipping documentation, customer communication and the later reconciliation of transactions created during an outage.
Rank #4
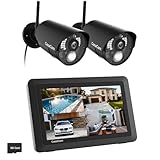
- True DIY DVR system with toucscreen monitor. Simply connect the camera to a power supply and experience the ease of use and peace of mind you’ve come to expect from CasaCam!
- See, hear and speak to people on your property from your 7" monitor, phone or tablet. Keep track of your property from anywhere at any time. System works locally without the need of Internet.
- Portable 7" touchscreen monitor with auto, manual and scheduled recording modes. Five seconds pre-record period ensures the event is fully captured. Rechargeable battery and SD card are included.
- System supports up to 4 cameras with single, split or quad display. Also compatible with CasaCam Spotlight Camera (SKU#VC1000). You can expand your system with add-on VC1000 Spotlight Camera to gain a useful security light feature!
- Smart motion detection uses dual sensors (heat and video motion) to minimize false alarms.
For enterprise buyers, the relevant categories include endpoint detection and response, identity security, incident response, immutable backup and recovery, operational-technology security and business-continuity planning. Stryker said it worked with Palo Alto Networks Unit 42 during its investigation. Other examples of relevant security categories include Microsoft Defender for Endpoint, Microsoft Entra ID, Rubrik Security Cloud and CrowdStrike Falcon.
No single security product would have guaranteed uninterrupted Stryker operations. The practical buying decision is a layered program combining identity protection, endpoint monitoring, network and environment segmentation, tested recovery and specialized incident response.
Recovery status and the financial takeaway
By March 23, Stryker said manufacturing capability was ramping quickly as critical lines and plants came back online. Reuters reported on March 26 that manufacturing was mostly restored and operations were improving toward full capacity.
That does not establish that every customer order, site, product line or backlog was immediately normal. The cited public materials also do not independently verify Stryker’s final long-term remediation status or total financial impact.
For hospitals, the central issue was availability and scheduling rather than evidence of unsafe products. For investors and supply-chain managers, the incident demonstrates how cyber risk can become an operational and financial risk even when a manufacturer’s products themselves are not compromised.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




