Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
State Farm’s 2019 incident was primarily a credential-stuffing attack: attackers used username-and-password combinations obtained elsewhere to try logging in to State Farm online accounts. State Farm said the credentials for affected users were valid, but that sensitive personal information was not viewable and no fraudulent activity was found during its review.
This is a historical incident reported on August 9, 2019—not automatically evidence of a new State Farm breach in 2026. The event was narrower than a confirmed theft of State Farm’s entire customer database, but it was still serious because reused passwords can unlock unrelated email, banking, payment, insurance, and other accounts.
What the State Farm notice said
The incident involved State Farm online accounts and a Notice of Data Breach sent to affected users. According to the sample notice filed with the California Attorney General, attackers used lists of user IDs and passwords obtained from another source, such as the dark web, to attempt access to State Farm accounts.
Recommended Free Tools
State Farm said it determined that the attacker possessed the valid username and password for the recipient’s account. The notice also stated that no sensitive personal information was viewable and that State Farm found no fraudulent activity after reviewing the account.
#1 Best Overall

- Requires 3 "AAA" batteries (included)
- Unit auto-locks for 30 minutes after 5 consecutive incorrect PINs
State Farm reset the affected passwords and instructed customers to create a new, unique password for State Farm and for every other service where the same credentials had been reused.
The incident in one sentence
State Farm disclosed confirmed account credentials in a credential-stuffing campaign, not a documented mass theft of its primary customer database.
That distinction matters. Calling the event simply a “State Farm data breach” can imply that attackers stole names, Social Security numbers, payment data, policy records, or the company’s entire customer database. The available notice does not establish that.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
What is credential stuffing?
Credential stuffing is an automated attack that takes advantage of password reuse:
- Criminals obtain username-password combinations from an unrelated breach, phishing campaign, leak, or underground marketplace.
- They use automated tools to test those combinations against another service.
- Some logins succeed because people reused the same password.
- The attacker can identify valid credentials even if the target company’s central database was never stolen.
In State Farm’s case, the notice described credentials coming from “other sources.” BleepingComputer characterized the activity as credential stuffing and reported that the first detected activity occurred on July 6, 2019, followed by activity on July 8, 12, 13, 14, 17, 19, 20, and 22.
A successful login is not automatically proof that an attacker viewed every part of an account or committed fraud. It is, however, proof that the credential pair was valuable enough to work—or to be confirmed as valid—and should no longer be trusted.
Rank #2
- Auto-Fill Feature: Say goodbye to the hassle of manually entering passwords! PasswordPocket automatically fills in your credentials with just a single click.
- Internet-Free Data Protection: Use Bluetooth as the communication medium with your device. Eliminating the need to access the internet and reducing the risk of unauthorized access.
- Military-Grade Encryption: Utilizes advanced encryption techniques to safeguard your sensitive information, providing you with enhanced privacy and security.
- Offline Account Management: Store up to 1,000 sets of account credentials in PasswordPocket.
- Support for Multiple Platforms: PasswordPocket works seamlessly across multiple platforms, including iOS and Android mobile phones and tablets.
Was State Farm’s own database breached?
What is established: attackers attempted to access State Farm online accounts, and State Farm confirmed valid credentials for affected users.
What State Farm reported: sensitive personal information was not viewable, and no fraudulent activity was found after its account review.
What the available notice does not establish: that attackers stole State Farm’s entire user database, gained unrestricted access to sensitive customer records, or accessed specific data elements such as Social Security numbers, driver’s-license numbers, bank-account details, addresses, or policy information.
It is also too broad to say that “nothing was accessed.” The notice confirms attempted access and validation of credentials. It says sensitive personal information was not viewable, but it does not provide a detailed account of every successful login, page visited, piece of account metadata exposed, or action attempted.
What information was involved?
| Question | What the available evidence shows |
|---|---|
| Were valid State Farm credentials involved? | Yes. State Farm said the attacker possessed a valid user ID and password for affected accounts. |
| Did the credentials come from State Farm? | The notice said the lists came from other sources. |
| Was sensitive personal information viewable? | State Farm said it was not. |
| Was fraud confirmed? | State Farm said its review found no fraudulent activity. |
| Were Social Security numbers, payment data, or policy details exposed? | The cited notice does not establish that those data elements were exposed. |
The most important risk was password reuse. A password confirmed at State Farm might also have worked at an email provider, bank, retailer, tax service, cloud-storage account, workplace system, or another financial-services company.
Quick wins for a faster PC:
Clear out junk files and repair common Windows errorsFree Scan →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →2019 timeline
- July 6, 2019: first detected activity, according to BleepingComputer.
- July 8, 12, 13, 14, 17, 19, 20, and 22: additional attack activity reported by BleepingComputer.
- August 2019: State Farm’s sample customer letter was dated “August xx, 2019.” The publicly available sample uses a placeholder, so it should not be treated as the precise mailing date for every customer.
- August 9, 2019: Dark Reading published the article titled “State Farm Insurance Notifies Users About a Breach but Doesn’t Panic.”
The California Attorney General’s breach-reporting system concerns notices involving California residents and does not by itself prove that every State Farm customer nationwide was affected.
Rank #3

- NEVER FORGET A PASSWORD AGAIN: Almost every App. has a password, it is almost impossible to remember all the password log in details. This password book is specifically designed to help you create secure passwords and store all your passwords safely in one place. You will never forget your password log-in details again with this password keeper.
- ALPHABETICAL A-Z TABS FOR QUICK ACCESS: Alphabetical tabs design allows you to store your passwords alphabetically so you can find what you want faster, no more annoying searches!
- ANONYMOUS WITHOUT ANY TITLE: On the outside, this password notebook organizer looks just like those writing journals, there is no title listed on the cover, so no one would know it's a password book. But we still recommend keeping the internet password logbook in a safe place such as a locked drawer or a shelf full of books.
- THICK NO-BLEED PAPER: This 5.2" x 7.6" password book contains 74 sheets of thick 120gsm paper that resists ink smearing, say goodbye to those cheap password books that bleed ink!
- PREMIUM QUALITY & PERFECT MEDIUM SIZE: This password journal comes with a high-quality leatherette hardcover, an elastic band, pen holder, ribbon bookmarker, and inner accordion pocket. It measures 5.2 inches wide and 7.6 inches long, which is the perfect size for your needs.
Why State Farm reset passwords
Resetting the affected State Farm passwords was a direct containment measure: it invalidated the known username-password combinations. Targeting accounts for which credentials had been confirmed was more focused than forcing every customer to change a password.
State Farm also said it implemented additional controls and continued evaluating its information-security measures. The cited materials do not specify every control, so it would be inappropriate to claim a particular security technology or policy change.
The password reset had limits. It did not automatically secure other accounts that used the same password, an email account used for password recovery, or an account where an attacker had already changed contact details.
What affected customers should do
- Reset the State Farm password through an official channel. The 2019 letter directed customers to type statefarm.com, choose Login, select Forgot Password, and complete the account-verification questions. Do not use an unexpected email link to begin the process.
- Create a password that is long and unique. Do not reuse it at any other website. A password manager can generate and store a different password for each account.
- Change reused passwords elsewhere. Start with your email account, then banking, payment, tax, government, workplace, insurance, and shopping accounts. Secure email especially quickly because it may be used to reset other passwords.
- Review the State Farm account. Check profile details, email addresses, phone numbers, payment settings, policy information, messages, and recent activity for changes you did not make.
- Review financial accounts. Check bank and card statements for suspicious transactions. A password-only notice does not prove that payment information was exposed, but monitoring is a sensible precaution.
- Watch for phishing. Criminals may use an old breach notice as a pretext to request passwords, Social Security numbers, payment details, or verification codes.
For help with the account, the 2019 letter listed 1-800-STATEFARM. Use contact information from State Farm’s official website or your trusted records rather than a phone number supplied in a suspicious message.
Should you freeze your credit?
The notice recommended vigilance for 12 to 24 months, regular review of accounts and free credit reports, and consideration of a security freeze.
A credit freeze is most relevant when a breach exposes information that can support identity verification or new-account fraud, such as a Social Security number or driver’s-license data. The available State Farm notice describes confirmed username-and-password credentials and says sensitive personal information was not viewable. That does not make a freeze inappropriate, but it means a freeze is not automatically necessary for every person based solely on this notice.
Rank #4

- NEVER FORGET A PASSWORD AGAIN - Clever Fox password journal will help you create secure passwords and keep them safe and organized. This password book allows you to store all your passwords and other computer information in one place to find it easily.
- ALPHABETICAL A-Z TABS - Alphabetic tab system makes it easy to find any password you need. The book also has sections for most important passwords, wireless & email settings, software license information & additional notes.
- ELEGANT, SMART, PRACTICAL & SECURE PASSWORD ORGANIZATION - This password keeper book has been designed to be anonymous without an obvious title on the cover. For added security there is space to write hints instead of the password itself.
- POCKET SIZE & PREMIUM QUALITY - This internet address and password logbook with tabs comes in pocket size (4.0x5.5 inches). The password notebook has an eco-leahter hardcover, elastic band, pen loop, bookmark, pocket for notes, and thick 120gsm paper.
- 60-DAY MONEY-BACK GUARANTEE - We will exchange or refund your password organizer if you aren’t satisfied with your password organization for any reason. Reach out to us via message to refund your internet password logbook.
A freeze generally must be placed separately with each of the three nationwide credit bureaus. Follow the instructions in your individual notice, particularly if it identifies additional information beyond the sample letter.
How to recognize a fake State Farm follow-up
State Farm’s current security guidance says customers should not reply to suspicious messages or provide personal information through unsolicited email, attachments, or pop-up windows.
For a legitimate password reset, navigate independently by typing the official address manually, using the official mobile app, or contacting a local agent through a trusted number. A genuine notification may tell you to reset a password, but it should not require you to email a password, Social Security number, bank login, payment details, or one-time security code.
State Farm says suspicious emails can be forwarded to [email protected]. If you already supplied information to a scam, change the affected password immediately, monitor your accounts, and consider contacting the credit-reporting agencies about a fraud alert.
What remains unknown
The public materials support a careful conclusion, not an all-encompassing one. They establish that State Farm accounts were targeted with credentials obtained elsewhere and that valid credentials were confirmed for affected users. They also record State Farm’s statement that sensitive personal information was not viewable and that no fraudulent activity was found.
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →They do not provide a complete account-level log showing whether every affected credential produced a successful login, what non-sensitive account information might have been visible, or whether every customer received exactly the same notice. Those limits are why “no sensitive personal information was viewable” is more accurate than “no information was accessed.”
Best Value
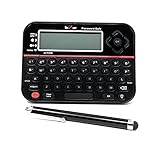
- Securely Remember All Your Passwords, Log-in's, User Names, ATM PIN Numbers and More
- Large Back-lit LCD Screen, QWERTY Keyboard - So Easy to Use
- Enter one PIN number and have access to 400 accounts. Search function included.
- Unit auto locks for 30 minutes after 5 consecutive incorrect PIN attempts
- Includes mini stylus for easier keypad entry
Tools that can reduce future credential-stuffing risk
You do not need a paid service to respond to this incident. The highest-value step is using a different password for every account, ideally with multifactor authentication or passkeys where supported.
A password manager such as Bitwarden, 1Password, or Proton Pass can generate and store unique passwords. Free and paid plans, features, and limits vary, so check each provider’s current terms. The important feature for this specific risk is not a brand name; it is the ability to stop reusing passwords.
Have I Been Pwned can help identify whether an email address appears in known breach datasets and can provide notifications. It does not replace password changes, account review, multifactor authentication, or credit monitoring.
Do these 3 things before closing this tab:
1Fix the driver behind crashes, sound loss and screen glitches2Clear out junk files and repair common Windows errors3Scan for outdated or missing drivers - takes under a minutePaid identity-monitoring services such as Aura may be useful for people dealing with broader identity-data exposure, but a bundled service is likely excessive for a notice limited to valid username-password credentials with no reported viewable sensitive personal information. No service can undo the 2019 exposure.
The broader personal-finance lesson
This incident illustrates why an old breach can create a new account-security problem years later. Criminals do not need to break into every target company directly if stolen credentials continue to work elsewhere.
For the State Farm incident, the evidence points to a narrower event than a confirmed mass theft of sensitive State Farm records. But “narrower” does not mean harmless: a reused password can connect an insurance login to accounts containing far more valuable personal and financial information. Unique passwords, secure recovery email, multifactor authentication, and prompt review of account changes are the durable protections.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.



