Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Jingle Thief is the name Palo Alto Networks Unit 42 gave to a financially motivated campaign that targeted retailers and consumer-services companies able to issue gift cards. Rather than relying primarily on malware or a newly discovered cloud vulnerability, the attackers stole employee credentials and tokens, abused legitimate Microsoft 365 features, learned internal gift-card procedures, and used compromised accounts to issue unauthorized high-value cards.
Public reporting confirms large-scale activity, including losses of up to $100,000 per day at certain companies reported by Microsoft. However, Unit 42 has not published one independently verified campaign-wide total proving that Jingle Thief stole “millions” of dollars. That figure should be treated as a qualified aggregate estimate, not an established single loss figure.
What is Jingle Thief?
Jingle Thief is a campaign name, not necessarily the confirmed name of one formal criminal organization. Unit 42 tracks the activity as CL-CRI-1032 and describes it as a cloud-based gift-card fraud campaign targeting global retail and consumer-services enterprises.
Recommended Free Tools
Unit 42 assesses with moderate confidence that the activity overlaps with groups publicly tracked as Atlas Lion and STORM-0539. Those labels should not be treated as definitively interchangeable: different security companies may group activity differently, and attribution is an assessment rather than a legal finding. Unit 42 also associated much of the infrastructure with Morocco, but that does not prove that every participant was located there.
#1 Best Overall
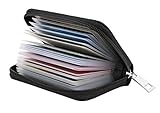
- Material: Genuine leather and PVC card slots.
- Size: 4.72"*3.15"*0.7" (12*8*1.8 CM)
- Large Capacity: The card holder has 26 cards slots. It is enough room for your ID card, credit cards, gift cards and dicounted cards. Small size is perfect to fit in your pockets or handbags.
- RFID Blocking: RFID Blocking designed lining keeps your vital information Secure. Be safe and protected from Electronic Pick pocketing.
- Great Gift Idea: Great gift for mother, daughter, grandmother and so on.
The coordinated activity described by Unit 42 included an attack wave in April and May 2025. Its report was published on October 22, 2025. In one customer environment, the attackers reportedly retained access for approximately 10 months and compromised more than 60 user accounts.
Unit 42’s campaign report provides the primary account of the activity.
Why gift cards are valuable targets
Gift cards combine several features that are attractive to fraudsters:
- They can be issued digitally and transferred quickly.
- They are easy to resell or redeem.
- They are not always directly linked to a named bank account in the way a conventional payment card is.
- Fraudulent issuance can resemble a legitimate business transaction.
- An employee account may already have permission to create or approve cards.
- Holiday and promotional periods increase transaction volume and time pressure.
Microsoft has described seasonal activity around Memorial Day, Labor Day, Thanksgiving, Black Friday, and Christmas. Those periods can make unusual issuance harder to spot because legitimate gift-card activity is already elevated. Microsoft’s reporting also says STORM-0539’s primary motivation was to steal and sell gift cards online at a discount.
For a business, the exposure is not limited to the face value of a card. Costs can include chargebacks or refunds, customer remediation, investigation, lost inventory, accounting corrections, and reputational damage.
Rank #2

- 【Premium 50-Count Pack】 Each package contains 50 high-quality window gift card sleeves, meticulously designed to meet your daily, business, or festive event needs. These envelopes are perfectly sized to accommodate standard credit cards and various gift cards, offering convenience and versatility.
- 【Clear View Window Design】 Featuring a distinctive transparent film window, these envelopes allow for a clear display of enclosed gift cards, membership cards, or cherished photos without removal, adding a touch of sophistication and professionalism. An ideal choice for conveying sentiments and enhancing presentation.
- 【Quality Kraft Paper Material】 Crafted from durable and eco-friendly kraft paper, these gift card envelopes provide a pleasant tactile experience and a smooth surface for writing, resisting tears and wear. The classic kraft paper tone exudes a simple yet elegant charm, suitable for diverse occasions and reflecting refined taste.
- 【Versatile & Widely Applicable】 Excellently suited for business invitation cards, party greeting invitation cards, holiday greeting cards, thank you notes, and more. Whether for corporate functions, weddings, birthday celebrations, Christmas, Thanksgiving, or as everyday small mailing envelopes, they serve as an ideal medium for your well wishes and messages.
- 【Convenient & User-Friendly】 The gift card holder design ensures portability and ease of mailing. Neat edges, these envelopes are simple to seal securely, safeguarding their contents. A practical solution for individuals, small businesses, or event organizers seeking elegant gift card holders.
How the Jingle Thief attack worked
The campaign is best understood as an identity and business-process intrusion, not a conventional malware breach.
- Reconnaissance: Attackers identified organizations that issued or managed gift cards and studied likely employees, applications, and workflows.
- Phishing and smishing: Tailored emails and text messages directed targets to fake Microsoft 365 or other enterprise-login pages.
- Credential or token theft: The lures were designed to capture usernames, passwords, and, in some activity attributed to STORM-0539, secondary authentication tokens through adversary-in-the-middle phishing.
- Cloud-account access: Attackers signed in with valid credentials and used the victim’s Microsoft 365 environment rather than immediately deploying malware.
- Cloud reconnaissance: They searched SharePoint and OneDrive for financial procedures, gift-card instructions, ticketing information, exports, and details about VPN, Citrix, virtual-machine, and internal-tool access.
- Internal lateral movement: Compromised mailboxes were used to send convincing messages to colleagues and expand access.
- Persistence: Attackers created forwarding or inbox rules, abused identity features, and sought access to additional users and applications.
- Fraudulent issuance: Accounts with suitable permissions were used to create or approve high-value gift cards.
- Monetization: Cards could be sent to attacker-controlled destinations, resold, redeemed, or potentially used in other laundering arrangements. Unit 42 presents some of these outcomes as assessments rather than verified results for every card.
How internal phishing made the attack harder to recognize
A message from a compromised colleague can carry more credibility than an email from an unknown external sender. After studying an organization’s terminology and procedures, attackers reportedly used lures resembling:
PC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware match- ServiceNow ticket-completion notifications;
- account-inactivity warnings;
- access-request messages; and
- approval prompts.
The recipient may see a familiar name, realistic internal language, and a link that appears related to an existing work process. That is why employee training alone is not enough. Organizations also need controls that detect unusual internal sending, suspicious login links, new forwarding rules, and access to sensitive collaboration content.
What “cloud infrastructure exploitation” means here
The phrase can suggest that attackers found a remotely exploitable flaw in Microsoft Azure, Microsoft 365, or a gift-card platform. The public Unit 42 and Microsoft material does not establish that Jingle Thief used a zero-day vulnerability in Microsoft’s cloud infrastructure.
The documented pattern was primarily abuse of legitimate capabilities:
Rank #3

- Perfect Size: Small envelopes (4 x 2-3/4 inches) that fit gift cards and money perfectly.
- Purchase reasons: Use for gift-giving, advent calendars, handmade cards, or creative projects like the 100 envelope challenge.
- Variety of Colors: Bold and pastel colors that make a visually stunning impact on any occasion.
- Great quality Material: Made from durable Kraft paper material.
- Customer Satisfaction: Trust the ACSTEP brand for quality gift card envelopes that meet all your needs.
- compromised Microsoft 365 identities;
- valid sessions and stolen authentication tokens;
- SharePoint and OneDrive search;
- mailbox forwarding and inbox rules;
- internal distribution lists;
- device registration and identity persistence; and
- legitimate cloud resources used to support phishing.
This distinction changes the defense. Patching remains important, but patching alone will not stop an attacker who has obtained a valid identity with access to a gift-card system. The relevant evidence may be in Entra ID, Exchange, SharePoint, OneDrive, SaaS audit logs, and transaction records rather than on a machine showing obvious malware.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesWhat is actually documented about the losses?
“Stole millions” is a common headline-level description, but it should not be presented as a precisely verified campaign total without a source showing the underlying accounting.
The strongest public figures currently described in the supplied primary reporting are:
- Microsoft observed gift-card activity associated with STORM-0539 increase by 30% between March and May 2024.
- Microsoft reported losses of up to $100,000 per day at certain companies.
- Unit 42 described high-value card issuance attempts across multiple programs.
- Unit 42 reported approximately 10 months of access and more than 60 compromised accounts in one customer environment.
These figures are not interchangeable. An attempted issuance is not necessarily an issued card; an issued card is not necessarily redeemed; and a card’s face value is not necessarily the victim’s confirmed loss. “Potentially millions” or “multi-million-dollar exposure” is more accurate than stating an independently verified campaign-wide total.
Microsoft’s gift-card fraud overview is available in its Cyber Signals report.
Rank #4

- High Capacity: With each compartment having the capacity to hold up to 40 cards, our one pack business card holder can store a total of almost 160 cards. You can now carry all your business cards in one convenient location.
- Product Size: Our business card holders come in a set of 2 with 4 compartments in each holder, allowing you to easily organize your business cards. The rack has 4 pockets that are perfect for standard-sized business cards. Measuring at 4.0 × 3.9 × 3.6 inches, it is compact enough to fit on any desk or display at exhibitions.
- Efficient Card Organizer: Showcase your business cards in style with our sleek and sophisticated business card stand. It is an ideal way to keep your working environment neat and tidy, and is perfect for small businesses and individual departments.
- Crystal Clear Appearance: Our business card display holder features a clear plastic acrylic that allows you to view the entire front of a business card with ease. It is an impressive way to leave a great first impression with clients and colleagues.
- Superior Material Quality: Our business card stands are crafted with premium clear acrylic, ensuring its durability and sturdiness. If you happen to receive a broken business card stand, please do not hesitate to contact us and we will be happy to provide you with replacement or refund.
Why gift-card issuance deserves financial-system controls
Many companies protect payment databases carefully but treat gift-card administration as an ordinary marketing or customer-service function. Jingle Thief shows why that separation can be dangerous. A gift-card portal should be treated as a high-value financial system, even when the cards are issued through a legitimate promotional or customer-support program.
Useful controls include:
- Separate duties: Do not allow one employee identity to create and approve unusually large or unusual batches.
- Set limits: Apply per-user, per-department, per-application, and time-based issuance caps.
- Add risk-based friction: Require a second approval or cooling-off period for large batches, new recipients, unusual geographies, or activity outside normal hours.
- Reconcile transactions: Match issued cards with approved orders, fulfillment records, recipient information, and redemption activity.
- Preserve audit trails: Record the issuer, approver, device, session, recipient, card state, and redemption event.
- Act quickly: Suspend or void unredeemed cards as soon as compromise is suspected.
Applying the same approval friction to every holiday transaction may slow legitimate operations. Risk-based thresholds are usually more practical: routine low-value issuance can remain fast, while high-value or anomalous activity receives additional review.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Priority defenses for retailers and consumer-services companies
1. Harden identities and sessions
- Require phishing-resistant MFA, preferably FIDO2 security keys or passkeys where supported.
- Use risk-based Conditional Access and sign-in-risk policies.
- Restrict device registration and review or approve new devices.
- Alert on MFA-method changes, resets, suspicious enrollment, and unusual device or location combinations.
- Separate gift-card administration from ordinary employee identities.
- Use just-in-time or time-limited elevation for high-value issuance and approval.
- Monitor sessions and tokens, not only password changes.
Phishing-resistant MFA is stronger than SMS or push-based approval, but it requires enrollment, recovery, compatibility, and help-desk planning. MFA should not be treated as sufficient protection if attackers can steal sessions, register devices, or abuse recovery processes.
2. Monitor email and collaboration services
- Alert on new mailbox-forwarding and suspicious inbox rules.
- Block or tightly control external auto-forwarding, with documented exceptions.
- Detect unusual internal bulk mail and messages that imitate IT-ticketing workflows.
- Protect shared mailboxes and high-value employees with stronger authentication and monitoring.
- Use known internal channels to verify unexpected login, access, or approval requests.
Blocking all forwarding can disrupt legitimate business processes. A better approach may be to restrict it by default, document exceptions, assign an owner, and monitor every exception.
Free tools Windows power users keep installed
One-click scans. No signup required.
3. Correlate identity and transaction telemetry
Security and fraud teams should connect cloud activity to the gift-card ledger. Investigations should ask:
Best Value

- 💳 QUICK ACCESS & LARGE CAPACITY HOLD UP 1-12 CARDS: This mens wallet designed with enhanced enjection mechanism button to pop up cards quickly. The aluminum card holder holds 4-6, depends on the number of embossed cards, and the expandable metal backplate holds 5-6 additional cards. The actual capacity depends on the card thickness.
- 💳 ULTRA THIN PROFILE (SLIM WALLET FOR MEN): The minimalist tactical wallet is very thin and can be carried comfortably in a pocket. The aluminum cardholder size is 3.9*2.5*0.5in,weight only 2.6oz. And expandable backplate designed for additional storage. Ditch the bulk, less is more.
- 🔒 RFID & NFC BLOCKING: This smart wallet use advanced aluminium technology to protect your cards from unauthorized and contactless scanning. Stop thieves from cloning your bank cards and prevent data theft.
- 💳 KEEP CARD TIGHTLY: Our pop up wallet with inside silicone strip that keeps your cards to be held tightly compared with normal felt. No worry cards will fall out.
- 🎁 PERFECT PRESENT IDEA: Our minimalist wallets packed with a pretty box. Aluminum wallet for men is a great present for boyfriend, brother, son, husband, dad, or your male friends on christmas, birthdays, anniversaries, and father's Day.
- Which accounts signed in from unusual devices, locations, or IP ranges?
- Were new authentication methods or devices registered?
- Were MFA settings changed or reset?
- Were forwarding rules or hidden inbox rules created?
- Did compromised accounts send internal phishing messages?
- Which SharePoint, OneDrive, VPN, Citrix, or gift-card documents were accessed?
- Which cards were created, modified, emailed, downloaded, or redeemed?
- Were issuance privileges escalated, delegated, or used outside normal hours?
- Did the same device fingerprints or sign-in patterns appear across related accounts?
- Can unredeemed cards be suspended or voided immediately?
Geographic blocking can provide useful detection context, but it is a weak primary control. An apparent association with Morocco-based infrastructure does not mean every malicious session will originate in Morocco.
What employees should watch for
- Unexpected Microsoft 365 or ServiceNow login requests.
- Urgent warnings that an account will become inactive.
- Requests to approve access that were not initiated by the employee.
- Messages from colleagues containing unusual login links.
- MFA prompts or device-registration notices the employee did not start.
When one of these appears, do not use the message’s link to investigate. Open the known corporate portal directly or verify the request through a trusted internal channel, then report it to the security team.
What remains unknown
Public reporting does not identify every victim, establish a definitive campaign-wide loss total, or prove that a Microsoft cloud software vulnerability was exploited. It also does not justify saying that every related incident used exactly the same authentication or persistence method.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →The more defensible conclusion is narrower and more useful: Jingle Thief demonstrates how a stolen cloud identity can become a path into a company’s internal procedures and high-value gift-card workflows. Retailers need to protect not only accounts and endpoints, but also the approvals, limits, audit trails, and redemption controls that determine whether a compromised account can turn access into money.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.



