The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Cellebrite completed its acquisition of Corellium on December 1, 2025. The deal’s $170 million base enterprise value comprised $150 million in cash and $20 million in Cellebrite equity; a further $30 million is payable only if performance milestones are met. That makes roughly $200 million the maximum potential value—not the fixed cash price.
What happened—and when
Cellebrite DI Ltd., the Israel-headquartered digital-investigation company traded on Nasdaq as CLBT, announced a definitive agreement to acquire U.S.-based Corellium on June 5, 2025. The companies initially expected to close in summer or the third quarter, subject to regulatory review and other customary conditions. The acquisition closed on December 1, and Cellebrite announced completion the next day. Corellium became a wholly owned Cellebrite subsidiary. Cellebrite’s announcement and its completion notice document the timeline and terms.
What the $200 million figure means
| Deal component | Amount | Meaning |
|---|---|---|
| Cash paid at closing | $150 million | Cash consideration paid for the acquisition |
| Equity consideration | $20 million | Converted into Cellebrite equity |
| Base enterprise value | $170 million | The announced value before potential milestone payments |
| Contingent consideration | Up to $30 million | Additional cash tied to performance milestones over two years after closing |
| Maximum potential value | Approximately $200 million | Base value plus the full potential earn-out |
These figures describe different parts of the transaction and should not be conflated: enterprise value, cash paid, equity issued, and contingent consideration are not interchangeable. The additional $30 million is not guaranteed. Cellebrite’s annual filing describes the acquisition accounting and contingent consideration; it also allocated approximately $58 million to acquired technology in the purchase-price allocation. That accounting allocation is not the purchase price or a separate valuation of Corellium. Cellebrite’s filing with the SEC provides further detail.
Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesWhat Corellium does
Corellium makes Arm-based virtualization technology, including hypervisor software used to create virtualized environments for mobile and other Arm-based systems. Security researchers and developers can use such environments to examine operating systems, test applications, and investigate vulnerabilities without relying exclusively on a physical device for every test. Potential applications include iOS and Android security work, secure software development, automotive systems, and Internet-of-Things devices. Cellebrite described Corellium’s technology in its transaction disclosure.
#1 Best Overall

- The Cellphone Investigation Kit is a complete solution for accessing and preserving data from virtually any mobile device. One kit covers iPhones, Android phones, GSM SIM cards, and photo backup — giving investigators, IT professionals, and parents everything they need in a single package.
- The included iRecovery Stick accesses data directly from iPhones and iPads running up to iOS 26.x, pulling contacts, text messages, call logs, saved passwords, WiFi networks, photos, the Deleted Photos folder, and more. Runs entirely on your Windows PC — no software is installed on the target device and no trace is left behind.
- The Phone Recovery Stick analyzes Android devices, recovering contacts, messages, photos, call logs, and more from a wide range of Android smartphones and tablets. Connect the target Android device to your Windows PC alongside the stick to begin extraction and data analysis.
- The SIM Card Seizure reader pulls data stored directly on GSM SIM cards, including contacts, SMS messages, call history, carrier information, and SIM serial numbers. Compatible with SIM cards from any carrier — including older flip phones and prepaid devices — making it essential for cases involving old phones that store data on SIM cards.
- The Photo Backup Stick completes the kit with fast photo and video backup from phones, tablets, and even computers, preserving visual evidence without requiring a PC or special software. All four tools work together to give you comprehensive mobile device coverage from a single professional investigation kit.
Calling Corellium simply an “iPhone simulator” misses the point. Its platform is used for security research and testing in virtualized operating-system environments, not just ordinary app previews. But virtualization is not a perfect stand-in for every physical handset. Hardware-backed security features, secure enclaves, baseband behavior, sensors, boot chains, and vendor-specific implementations may differ or be absent. A virtual environment can help researchers test and investigate; it does not guarantee that a vulnerability will work on a production device.
Why Cellebrite wanted it
Cellebrite sells digital-forensics and digital-investigation products to public-safety organizations, government and intelligence agencies, defense customers, and private-sector organizations. Its tools support legally authorized investigations, including extracting and analyzing digital evidence from mobile devices. That is distinct from Corellium’s virtualization and security-testing technology, even if the capabilities may complement one another.
Rank #2

- The PBN-TEC Digital Investigation Kit is a comprehensive eight-tool investigation system trusted by law enforcement agencies, private investigators, IT security professionals, legal teams, and even concerned parents. One kit covers mobile device extraction, computer investigations, evidence collection, illicit content detection, audio monitoring, and secure file deletion — no additional software purchases required.
- The iRecovery Stick extracts and investigates data from iPhone and iPad devices, the Phone Recovery Stick handles Android phones and tablets, and the SIM Card Seizure analyzes data from virtually any GSM SIM card. Together these three tools provide complete mobile device investigation coverage from a single kit, including contacts, messages, call logs, and photos.
- The Data Recovery Stick recovers deleted files from any Windows OS, the Voice Logger installs an audio monitoring application onto any Windows computer, and the Data Shredder Stick securely deletes files and wipes storage when the investigation is complete. All three tools work on Windows XP or newer with no additional software required.
- The Capturra Action Drive 1TB automatically collects targeted file types from virtually any device, serving as both an evidence storage drive and a targeted file collection tool for focused investigations. The XXX Detection Stick then scans the collected evidence for illicit content, categorizing results into Low Suspect, Suspect, and Highly Suspect for review.
- The Digital Investigation Kit includes everything needed to begin an investigation immediately — a Data Cable Kit with iPhone, USB-C, and Micro USB cables, a universal SIM Card Adapter compatible with all SIM card sizes, and a Softshell Compartmentalized Protection Case to organize and transport all eight tools securely.
Cellebrite said Corellium could help it identify mobile vulnerabilities and exploits more quickly, add virtual-device capabilities, and expand into mobile security, DevSecOps, and markets such as automotive and IoT. The strategic fit is that Corellium supplies a controlled environment for testing and research, while Cellebrite brings investigative products and established government and enterprise relationships. That rationale is a plausible explanation of the deal, not evidence that every intended integration has already been delivered.
Recommended Free Tools
The companies’ customer bases are not identical. Corellium’s potential users include application-security teams, penetration testers, and researchers; Cellebrite’s core business serves investigation and forensics customers. Whether Corellium can retain independent appeal among researchers while becoming part of a digital-forensics business is one of the commercial questions raised by the acquisition.
Rank #3
- The PBN-TEC Digital Investigation Kit is a comprehensive eight-tool investigation system trusted by law enforcement agencies, private investigators, IT security professionals, legal teams, and even concerned parents. One kit covers mobile device extraction, computer investigations, evidence collection, illicit content detection, audio monitoring, and secure file deletion — no additional software purchases required.
- The iRecovery Stick extracts and investigates data from iPhone and iPad devices, the Phone Recovery Stick handles Android phones and tablets, and the SIM Card Seizure analyzes data from virtually any GSM SIM card. Together these three tools provide complete mobile device investigation coverage from a single kit, including contacts, messages, call logs, and photos.
- The Data Recovery Stick recovers deleted files from any Windows OS, the Voice Logger installs an audio monitoring application onto any Windows computer, and the Data Shredder Stick securely deletes files and wipes storage when the investigation is complete. All three tools work on Windows XP or newer with no additional software required.
- The Capturra Action Drive 1TB automatically collects targeted file types from virtually any device, serving as both an evidence storage drive and a targeted file collection tool for focused investigations. The XXX Detection Stick then scans the collected evidence for illicit content, categorizing results into Low Suspect, Suspect, and Highly Suspect for review.
- The Digital Investigation Kit includes everything needed to begin an investigation immediately — a Data Cable Kit with iPhone, USB-C, and Micro USB cables, a universal SIM Card Adapter compatible with all SIM card sizes, and a Softshell Compartmentalized Protection Case to organize and transport all eight tools securely.
What the acquisition does—and does not—mean for phone security
Cellebrite’s tools are associated with extracting data from locked or encrypted devices in investigations. Corellium’s environments can support testing and vulnerability research. Bringing those areas together could help Cellebrite develop or improve investigative and security capabilities, but the acquisition does not establish that Cellebrite can unlock every iPhone or Android device.
Virtualization is not access to production-device encryption keys, a universal bypass, or a guarantee of access to any particular handset. Finding a vulnerability, developing an exploit, gaining access to a physical device, and extracting usable forensic data are separate steps. Their success can depend on the device model, operating-system version, configuration, and the specific security protections involved. CyberScoop’s coverage discusses the firms’ security work and the concerns surrounding it.
Rank #4
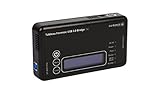
- Backlit Interface - Device status, device information, logical unit (LUN) select, and bridge information are easily accessible
- Supports USB 1.0/2.0/3.0, Flash Drives, Mass Storage Drives, and any "bulk storage" drive
- Kit Includes - TP2 Power Supply with US-Style power cord, TC-USB3 USB 3.0 (A to B) cable, 6 foot length, Soft-Sided bag and Quick Start Guide
- Hardware-Based USB 3.0 Write Blocker
Privacy, surveillance, and research concerns
The same capabilities that can support legitimate security research and legally authorized investigations can also raise concerns about surveillance, exploit development, responsible disclosure, and how governments or other customers use investigative tools. The deal therefore matters beyond its price: it links virtualization and security research more closely to a company whose products are used in digital investigations.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
That raises questions about customer trust and researcher independence, as well as how vulnerabilities are handled and disclosed. It does not, by itself, establish that Corellium’s research will be used for a particular purpose or that the merged company has produced a specific new capability. Those questions require evidence about products, policies, customers, and outcomes beyond the acquisition announcement.
Best Value

- TX2 Forensic Imager Kit Includes: TX2 Forensic Imager, TP8 Power Supply, US Power Cord, (x4) TC4-8-R4 Unified SATA/SAS Signal and Power Cable (Molex), (x2) TC-PCIE4-8 PCIe Adapter Cable, 8", (x2) TCA-USB3-AC USB 3.0-A to USB 3.1-C Cable Adapter, Velcro Cable Ties (TPKG-VCT-5), Microfiber Cloth (TPKG-CLOTH), Quick Ref Guide
- LIGHTNING-FAST PROCESSING AND IMAGING: Powered by parallel hash verification and concurrent imaging, the TX2 is up to 3.8x faster than its predecessor. Capture and verify evidence in record time across multiple jobs.
- STREAMLINED RECONFIGURATION PROCESS: The TX2 makes it easy to pivot between tasks with a simplified reconfiguration process. Wipe, format, or encrypt all in one.
- UNLIMITED CONCURRENT OR CONSECUTIVE QUEUEING: The TX2's architecture is built for multitasking, allowing for unlimited concurrent or consecutive queueing. Stack jobs back-to-back or run several at once.
- OPTIMAL POWER ALLOCATION: The TX2 intelligently allocates power with dynamic resource assessment to maintain peak performance during heavy workloads. Its dynamic power management evaluates task demands in real time, ensuring every imaging job runs at optimal speed.
Corellium’s dispute with Apple
Apple sued Corellium in 2019 over Corellium’s virtualized reproduction of iOS, including copyright-related claims. Corellium prevailed in a significant appellate ruling in 2023, and the parties later reached a confidential settlement, according to CyberScoop. Because the settlement was confidential, its terms and any continuing commercial restrictions should not be inferred. CyberScoop also reported, based on litigation documents, that Corellium had interacted with entities including NSO Group; that reporting should not be turned into an unsupported claim about Corellium’s current customers or activities.
Regulatory review and what remains unclear
The proposed acquisition was subject to review by the Committee on Foreign Investment in the United States (CFIUS), as well as customary closing conditions. CFIUS reviews certain transactions involving foreign investment in U.S. businesses for national-security implications. The deal’s completion establishes that the transaction proceeded, but the public information cited here does not establish whether CFIUS imposed conditions or issued a public determination. Cellebrite’s original announcement identified CFIUS review as a condition.
The acquisition’s completion does not answer every question about its effects. The cited announcements and filing do not establish a full product roadmap, the extent of customer or employee retention, whether Corellium will remain available as an independent offering, or whether the earn-out will be paid in full. Cellebrite said the deal was not expected to materially affect its fourth-quarter or full-year 2025 outlook, in part because only about one month of Corellium revenue and costs would be included in that period. That statement is not evidence of a later revenue increase or of specific product results.
Free tools Windows power users keep installed
One-click scans. No signup required.
For developers and security teams, Corellium’s virtualization is not interchangeable with physical-device labs or general-purpose testing services; the right choice depends on how deeply they need to inspect and test a system. Cellebrite, meanwhile, is a digital-investigation vendor rather than a conventional app-testing platform.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.



