Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Scan for outdated or missing drivers - takes under a minute3Repair Windows errors before they cause bigger problemsSome links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Scania confirmed that attackers accessed its externally operated insurance application on May 28 and 29, 2025, using compromised credentials, and downloaded insurance-claim documents. On May 30, the attackers threatened Scania employees and later advertised or leaked the material. Scania said the operational impact was “very limited,” but the number of people affected and the exact information in the files were not established in the coverage reviewed.
What happened
- Third-party application: An external IT partner operated Scania’s insurance application,
insurance.scania.com. - Compromised account: An attacker used credentials belonging to a legitimate external user. Scania said its working assumption was that infostealer or password-stealer malware had captured those credentials.
- Unauthorized access: The account was used on May 28 and 29, 2025.
- Data download: The attacker downloaded documents relating to insurance claims.
- Extortion: On May 30, the attacker emailed several Scania employees from a Proton Mail address, threatening to disclose the data. A later message came from an unrelated compromised third-party email account.
- Publication attempt: An actor using the alias “Hensi” subsequently advertised or leaked the material on an underground forum.
Scania’s incident description was reported by BleepingComputer and summarized by INCIBE-CERT.
Was Scania’s whole network hacked?
The confirmed incident concerns a specific insurance application, not a demonstrated compromise of Scania’s entire corporate or vehicle-production network. The application was operated by an external IT partner. Available reporting does not show that manufacturing systems or Scania’s broader corporate environment were broadly breached.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Clear out junk files and repair common Windows errorsFree Scan →This distinction matters financially and operationally: a company can keep production and customer services running while still suffering a serious confidentiality or privacy incident involving claim records.
#1 Best Overall

- UPSCALED 4K FRONT + 1080P REAR DUAL DASH CAM: The ROVE R2-4K DUAL records the road ahead and behind at the same time. The front camera captures at 2.5K (QHD) and intelligently upscales to 4K (2160P) for higher-detail playback, while the rear camera records at Full HD 1080P. This is upscaled 4K, not native 4K, engineered to show sharper everyday detail than standard 1080P dash cams, so you can read license plates, signs, and surroundings in front and rear footage.
- SONY STARVIS 2 IMX675 SENSOR + SUPER NIGHT VISION: The front camera uses a Sony STARVIS 2 IMX675 5MP image sensor with a wide F1.5 aperture (F1.8 rear) and HDR to pull in more light for clearer low-light footage. This advanced sensor enhances nighttime clarity, helping capture license plates, road signs, and surrounding vehicles with greater reliability when driving after dark, through tunnels, or in dusk and dawn conditions.
- ULTRA FAST 5.8GHz WIFI/ UP TO 20MB/s DOWNLOAD SPEED: With its built-in dual-band 5.8GHz and 2.4GHz WiFi, you can use the ROVE dash cam app to view and manage dash cam recordings instantly on your iPhone and Android smartphone. Using the ROVE app, download your recorded videos directly to your smartphone at up to 20 MB/sec, then easily share them on social media with friends and family. Additionally, manage camera settings and update the latest firmware over-the-air via the ROVE App.
- CAR CAMERA WITH GPS: The new front and rear dashcam comes with built-in GPS, which enables you to view real-time live speed and compass on the 3” IPS wide camera screen. It records precise driving routes, locations, and speed stamps directly on the video so you can watch dashcam videos with GPS data using ROVE's free GPS Player on your PC or Mac & get additional evidence when you need it.
- FEATURES WITH STATE-OF-THE-ART TECHNOLOGY INCLUDED: Experience peace of mind with this front and rear car dash cam. It comes with a free 128GB microSD card and offers advanced features such as an f1.5 aperture, motion detection, G-sensor, seamless loop recording, emergency video lock, screen saver, live speed and compass direction, voice guidance, ring of threads for optional CPL filter, a built-in supercapacitor for extended product life, support for up to 1TB microSD cards, and many more.
What information was exposed?
Scania confirmed that insurance-claim documents were downloaded. It did not publish a complete inventory of the documents in the reports reviewed, nor did those reports establish how many people were represented.
Claim files can potentially include personal, financial, medical or vehicle-related information, depending on the claim and the insurer’s process. That is a risk possibility, not confirmation that every stolen file contained those categories. SC Media discussed those possibilities while noting the limits of the available detail.
Confirmed, claimed and unknown
| Status | What is established |
|---|---|
| Confirmed or reported by Scania | An incident involving the insurance application; use of a legitimate external-user credential; downloading of insurance-claim documents; extortion emails; taking the application offline; an investigation and notifications to relevant authorities. |
| Claimed by the attacker | A total of 34,000 files, offered for sale or publication. |
| Not established in the reviewed coverage | The number of affected people, the exact data categories, whether every advertised file was genuine, the ransom amount, whether negotiations occurred, whether Scania paid, and the attacker’s identity or group affiliation. |
What does “34,000 files” mean?
The 34,000 figure came from the threat actor and was not independently verified in the coverage reviewed. A file count is not a count of customers, claimants, employees or identities. It could include attachments, duplicates, exports, administrative material or unrelated files.
The Tool Desk
Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →ITPro and SecurityWeek attributed the number to the attacker rather than presenting it as an independently confirmed breach total.
Rank #2
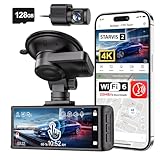
- [4K+1080P Dual Recording] REDTIGER F7N TOUCH captures your drive journey in stunning 4K UHD resolution with STARVIS 2 sensor 170° wide-angle view for the front dash cam and 1080P FHD resolution 140° wide-angle for the rear car camera. Equipped with WDR and HDR technology, the enhanced super night vision ensures better visibility even in low-light situations, providing you with reliable recordings day and night.
- [Voice Control & Touch Screen] F7NTOUCH dashcam features voice commands, allowing for hands-free control of your 4K car camera, which enhances safety by minimizing distractions. The dual camera dash cam also has smart touchscreen that can lock emergency video, turn on wifi, and capture scenery with one click. Redtiger also retains the buttons, multiple control methods are integrated.
- [Built-in GPS & 5.8GHz WiFi] Both Android and IOS users can connect to dashcam WiFi via the REDTIGER Cam app. Although the dash cam is installed wired, you can enjoy wireless control on your smartphone, faster 20MB/s download speed and share your driving experiences in real-time with friends and insurance companies. Car recorder built-in GPS provides traceable location, speed, and accurate route in the recordings.
- [Loop Recording & G-Sensor] REDTIGER F7N TOUCH dual channel dash cam automatically overwrites the oldest footage when the memory is full, ensuring endless recording with the included 128GB card. With a built-in G-sensor that detects sudden movements or impacts, it automatically locks and protects the associated footage when an event is detected on the road, ensuring it won't be overwritten during loop recording.
- [24-hour Parking Monitoring*] REDTIGER Car dashboard camera offers G-Sensor Parking Mode that automatically record when it detects any collisions or sudden motion while vehicles is parked. Time Lapse Parking Mode provides continuous surveillance by offering a condensed overview of any events that may occur during parking periods. *Please note that the parking monitoring function requires a separate hardwire kit.
Was this ransomware?
The evidence describes credential misuse, data theft and extortion. There is no reported indication that attackers encrypted Scania systems or demanded payment to restore access. “Data-theft extortion” or “non-encrypting extortion” is therefore more accurate than conventional ransomware.
The alias “Hensi” identifies the account that advertised or leaked the material; it does not establish a real-world identity or criminal affiliation. CYJAX reported no clear basis for attributing the Scania activity to Scattered Spider. The fact that threat-intelligence reporting discussed attacks against insurance companies does not prove a connection.
Did Scania pay a ransom?
No payment is reported in the sources reviewed. They establish that demands were made and that data was later advertised or leaked, but not the amount demanded, whether talks occurred, whether Scania paid, whether anyone bought the files or whether all advertised material was authentic.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
How Scania responded
- The affected application was taken offline.
- Scania began an investigation.
- Relevant authorities and privacy regulators were notified.
- Scania assessed the impact as “very limited” at the time of its statement.
That assessment describes the company’s reported view at that point; it is not a published final forensic report. The reviewed coverage did not provide a final affected-population figure, a detailed notification program or a complete root-cause analysis. The response details were reported by BleepingComputer, ITPro and SecurityWeek.
Rank #3

- 4-Channel Dash Cam for Complete Vehicle Coverage: This dash cam is equipped with four Full HD 1080P cameras, capturing footage of the front, rear, left, and right sides of your vehicle simultaneously. The adjustable front cameras enhance visibility and offer flexible recording angles, including interior footage.
- Time-Lapse Recording & Parking Mode: With time-lapse recording, 60 minutes of footage is compressed into 1 minute, saving memory card space. Activate parking mode with the optional ACC hardwire kit (sold separately) for security when your vehicle is parked.
- Enhanced Night Vision & WDR Technology: The dash cam features advanced night vision and Wide Dynamic Range (WDR) technology for clear, balanced footage, even in low-light conditions. Eight infrared lights ensure optimal visibility, and WDR adjusts exposure to capture detailed images in varying lighting.
- Optional GPS for Real-Time Vehicle Tracking: Purchase the GPS logger (sold separately) to add location, speed, and time tracking, providing a visual representation of your vehicle's route. This feature is perfect for documenting travel details in case of incidents.
- 5GHz Wi-Fi & App Integration: Share videos easily via Wi-Fi using the mobile app for both iOS and Android devices. This feature allows for quick video downloads and sharing on your preferred platforms.
Who should pay attention?
Potentially relevant groups include people who submitted vehicle-insurance claims through Scania-related services, Scania Financial Services or insurance customers, claimants whose records were processed by the application, and employees or suppliers contacted by the attackers. Organizations using the same external provider or identity system may also review their own access logs.
None of these groups should be treated as definitively affected unless Scania, an insurer or a regulator contacts them or publishes confirmation.
What potentially affected people should do
- Verify contact independently. Use Scania’s or your insurer’s official website, policy documents or a known telephone number—not a link or number in an unexpected message.
- Expect targeted phishing. Be cautious with messages mentioning a claim, vehicle damage, reimbursement, policy cancellation or urgent payment.
- Do not seek the leaked files. Avoid criminal-forum links and alleged samples; opening or sharing stolen documents can expose you to malware and further privacy harm.
- Secure reused passwords. Change a password if you reused it on the affected service or elsewhere. The confirmed mechanism involved a compromised external-user credential, not necessarily every claimant’s login.
- Turn on strong MFA. Prefer phishing-resistant multifactor authentication where a service supports it.
- Monitor accounts if notified of sensitive exposure. Review financial, insurance and identity accounts when Scania or a regulator confirms that information creating fraud risk was involved.
- Preserve evidence. Keep suspicious emails, headers, phone numbers and attachments, and report them to the organization or appropriate authorities.
What organizations can learn
The incident points to an identity and third-party access problem rather than a patching issue alone. Useful controls include multifactor authentication for external users, least-privilege permissions, rapid credential revocation, monitoring for unusual bulk downloads, session and conditional-access controls, and contractual security and incident-response arrangements with technology partners.
Free tools Windows power users keep installed
One-click scans. No signup required.
The available reporting does not identify the partner, describe its controls or establish how any infostealer infection occurred, so responsibility for the initial compromise should not be assigned beyond the confirmed facts.
What remains unresolved
- How many individuals, if any, were represented in the downloaded files.
- Whether medical, financial, identification or other sensitive data appeared in particular documents.
- Whether the full 34,000-file claim was genuine, complete or duplicated.
- Whether the material was sold, how much was demanded and whether any payment was made.
- Who operated under the “Hensi” name and whether the actor belonged to a larger group.
- What final forensic and remediation findings Scania or authorities may publish.
The defensible conclusion is limited but clear: Scania confirmed unauthorized downloading of insurance-claim documents from an externally operated application, followed by an extortion attempt and alleged leak. The scope of personal-data exposure was still undetermined in the reporting reviewed.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.



