What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
Some links on this page are affiliate links: if you buy through them we may earn a commission, at no extra cost to you.
Short answer: A report published on August 19, 2025 said a seller was advertising login credentials for what they claimed were millions of PayPal accounts for about $750, with data reportedly current as of May 2025. That does not establish that PayPal suffered a breach. The listing’s authenticity, origin, number of unique accounts, and continued usability were not independently verified in the available reporting.
PayPal users should treat the report as a warning to secure accounts—especially where passwords were reused, suspicious activity has appeared, or a device may be infected—but not as proof that every PayPal customer was affected.
What was reportedly being sold?
The reported listing allegedly offered credentials for “millions” of PayPal accounts at a price of approximately $750. The seller reportedly claimed that the information was current as of May 2025. Those details describe an advertisement and a seller’s claims, not a verified impact count.
Free tools Windows power users keep installed
One-click scans. No signup required.
The available report does not establish exactly what the collection contained. It is unclear whether the records included only email addresses and passwords, or also PayPal-specific account information, browser cookies, session tokens, autofill data, payment-card details, bank information, or identity data. The reporting also did not independently validate samples, explain the database structure, establish how many records were unique, or prove that the credentials still worked.
#1 Best Overall

- POWERFUL SECURITY KEY: The Security Key C NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key C NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key C NFC via USB-C and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
Credentials and account data should not be tested through criminal marketplaces or by attempting unauthorized logins. Doing so can expose you to malware, scams, or legal risk.
The original coverage and related PayPal reporting should therefore be read as reporting on an alleged sale—not confirmation of a PayPal security incident.
Is this a confirmed PayPal breach?
No—not on the evidence available in that report. A criminal listing that uses PayPal’s name is not, by itself, evidence that PayPal’s servers were penetrated.
Crashes, No Sound, or Screen Glitches?
Random freezes, missing sound and display glitches usually trace back to one bad driver. Find and replace yours safely.Free scan · under a minutePC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11Several different events can produce a collection marketed as “PayPal accounts”:
Rank #2
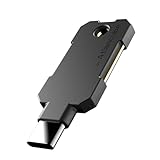
- PHISHING-RESISTANT 2FA: Cryptographically binds to real domains, making phishing attacks impossible unlike SMS codes or authenticator apps.
- 3-SIDE CAPACITIVE TOUCH: Tap the end, left, or right side to authenticate, so it works in any orientation or crowded USB port.
- MULTI-COLOR LED INDICATOR: Blue means ready, blinking blue means tap now, green means success, and red means error for instant status feedback.
- IP68 WATERPROOF & BATTERY-FREE: Crush-resistant one-piece construction survives daily carry on a keychain or in a bag for years without any batteries.
- UNIVERSAL COMPATIBILITY: Works with Google, Microsoft, Apple, GitHub, AWS, and any FIDO2 / U2F / WebAuthn service, storing up to 100 passkeys.
- Credential stuffing: Attackers use email-password pairs exposed in an unrelated breach against PayPal and other services. Reused passwords make this possible even when PayPal itself was not breached.
- Phishing: A victim enters PayPal credentials into a fake login page, giving them directly to the attacker.
- Infostealer malware: Malicious software extracts browser-stored passwords, cookies, autofill information, cryptocurrency-wallet data, and local files from an infected device.
- Recycled or compiled data: A seller combines older leaks and markets them as a new or PayPal-specific collection. The list may contain duplicates, expired passwords, or records from multiple incidents.
- A fraudulent listing: A seller may exaggerate the scale or advertise nonexistent data to collect cryptocurrency or other payments.
- A genuine PayPal-related compromise: This remains possible, but the available report does not demonstrate it.
A password theft, phishing campaign, or malware infection can put an individual PayPal account at risk without indicating a company-wide PayPal breach.
What would confirm the claim?
A stronger conclusion would require evidence beyond a seller’s advertisement, such as:
- A statement from PayPal confirming an incident or customer-notification process.
- A technical analysis by a named security researcher or threat-intelligence company.
- Lawfully obtained and independently verified samples containing previously unknown, valid records.
- Evidence connecting the data to a specific intrusion, malware family, phishing campaign, or collection operation.
- Database metadata consistent with a recent collection event.
- Proof that the records are not duplicates from older breaches.
- Independent confirmation of the claimed scale.
Without that evidence, the most accurate description is an unverified credential-dump claim. The absence of confirmation does not prove the listing is false; it means readers should not treat the seller’s claims as established facts.
Could infostealer malware be involved?
Yes, but this has not been established for this particular listing. Infostealers commonly target passwords saved in browsers, authentication cookies, autofill data, local files, and other information that can later be traded in criminal markets. A stolen PayPal login could consequently appear in a PayPal-branded collection even if PayPal’s systems were never accessed.
Rank #3

- HARDWARE 2FA AND MFA: FIDO Alliance Certified FIDO2 v2.1 with CTAP2 plus legacy U2F and CTAP1 for strong two-factor login and passwordless sign-in on services that support security keys
- BUILDING ACCESS ON ONE CARD: MIFARE DESFire EV2 4K applet with AES encryption adds office door and physical access control alongside digital authentication
- CERTIFIED SECURE ELEMENT: An NXP Common Criteria EAL6+ certified secure controller and Java Card platform protects your keys on a tamper-resistant chip
- DUAL INTERFACE SMART CARD: Contactless NFC ISO 14443 plus ISO 7816 contact reader support in an ISO 7810 ID-1 format that is passive and needs no battery
- SWISS ENGINEERED DESIGN: Built by Cryptnox as a single card for authentication and access control and backed by a 2 year warranty
The distinction matters:
- Password theft gives an attacker the username and password.
- Session-cookie theft may allow reuse of an authenticated browser session without knowing the password.
- Credential stuffing involves trying previously exposed password pairs against PayPal.
- Phishing tricks the user into submitting credentials to a fake site.
- Malware extracts information from an infected computer or phone.
Users who recently installed pirated software, unofficial browser extensions, fake updates, or unknown installers should take the possibility of device compromise seriously. Broader reporting on malware and infostealer-related credential trading provides context, but it does not prove the source of the alleged PayPal collection.
What PayPal users should do now
- Open PayPal directly. Use the official app or manually type the official website address. Do not use a link in an unsolicited email, text message, or social-media post. PayPal’s Security Center provides official account-security information.
- Change your PayPal password if it was reused anywhere, is old, or you suspect phishing or unauthorized access. Use a long, unique password that has never been used on another service.
- Change reused passwords elsewhere. Start with your email account, bank, card accounts, and any service that shared the PayPal password. Secure the email account first if it controls PayPal password recovery.
- Enable two-step verification in PayPal’s available security settings. It reduces the risk of password-only takeover, but it cannot fully stop phishing, malware, stolen sessions, or recovery abuse.
- Review account activity. Check recent payments, transfers, withdrawals, refunds, linked cards, linked bank accounts, profile changes, contact details, and security settings.
- Remove unfamiliar access. Review and remove unknown devices, browsers, app connections, and authorized third-party services where PayPal provides those controls.
- Check your email account. Look for unfamiliar forwarding rules, recovery-address changes, login alerts, or messages sent without your knowledge.
- Scan potentially infected devices. Update the operating system, browser, and security software. If malware is suspected, change important passwords from a clean device after remediation. A scan alone does not prove that stolen passwords or session tokens have been revoked.
- Contact PayPal through official channels if you find unfamiliar activity. Use the PayPal Help Center or Resolution Center—not a phone number supplied in a suspicious message.
How to recognize possible account takeover
Pay attention to password-reset messages you did not request, sign-ins from unfamiliar devices or locations, changed email addresses or phone numbers, repeated two-step-verification prompts, unknown payments or withdrawals, newly linked cards or bank accounts, and PayPal messages you did not send.
A genuine PayPal notification may be triggered by an attacker using your account, while a fake notification may simply be phishing. The safe approach is the same: do not click the message, open PayPal independently, and inspect the account.
If money was taken
- Contact PayPal through the official app or website and report unauthorized activity or open a dispute.
- Contact the linked bank or card issuer promptly if the transaction used that account.
- Change your PayPal and email passwords from a clean device and enable two-step verification.
- Save screenshots, sender addresses, URLs, dates, transaction IDs, and support-case details before deleting suspicious messages.
- Report related identity theft or scams to the appropriate authorities. U.S. residents can consult IdentityTheft.gov for recovery guidance.
Can you check whether your email appeared in a breach?
You can check an email address against known breach datasets at Have I Been Pwned. A clean result is not proof that the PayPal claim is false or that your account is safe: a newly advertised private dump may not be included, and the service cannot certify the authenticity or absence of a specific PayPal credential listing.
Rank #4

- POWERFUL SECURITY KEY: The Security Key NFC is the essential physical passkey for protecting your digital life from phishing attacks. It ensures only you can access your accounts.
- WORKS WITH 1000+ ACCOUNTS: Compatible with Google, Microsoft, and Apple. A single Security Key NFC secures 100 of your favorite accounts, including email, password managers, and more.
- FAST & CONVENIENT LOGIN: Plug in your Security Key NFC via USB-A and tap it, or tap it against your phone (NFC) to authenticate. No batteries, no internet connection, and no extra fees required.
- TRUSTED PASSKEY TECHNOLOGY: Uses the latest passkey standards (FIDO2/WebAuthn & FIDO U2F) but does not support One-Time Passwords. For complex needs, check out the YubiKey 5 Series.
- BUILT TO LAST: Made from tough, waterproof, and crush-resistant materials. Manufactured in Sweden and programmed in the USA with the highest security standards.
Never submit a password to an unknown “PayPal breach checker.” Fake checking pages may be designed to collect the very credentials they claim to investigate. A breach-checking result also does not replace changing reused passwords, enabling two-step verification, reviewing PayPal activity, or checking a potentially infected device.
What about PayPal’s earlier regulatory matter?
Secondary coverage also referenced a January 2025 regulatory matter involving a reported $2 million fine against PayPal over exposure of sensitive customer information. That matter should be treated as separate from the later alleged credential sale unless a primary source explicitly connects them. Different dates, data types, systems, and causes should not be merged into one incident without evidence.
A practical credibility scale
| Assessment | What it would mean |
|---|---|
| Confirmed | PayPal or a regulator acknowledges an incident, and named independent experts validate the records and their origin. |
| Plausible but unconfirmed | Some records appear current or the dataset resembles infostealer or credential-stuffing collections, but provenance and PayPal involvement remain unverified. |
| Weak or misleading | The seller provides no verifiable evidence, records are old or duplicated, or the claim appears only in reposts citing one another. |
On the available evidence, the August 2025 report belongs in the unverified category. That classification does not make account-protection steps unnecessary: an individual account can be compromised through password reuse, phishing, malware, or stolen sessions regardless of whether PayPal suffered a breach.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Quick Recap
Sources and further guidance
- Neowin PayPal coverage
- PayPal Security Center
- PayPal Help Center
- Have I Been Pwned
- CISA account-security guidance
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.



